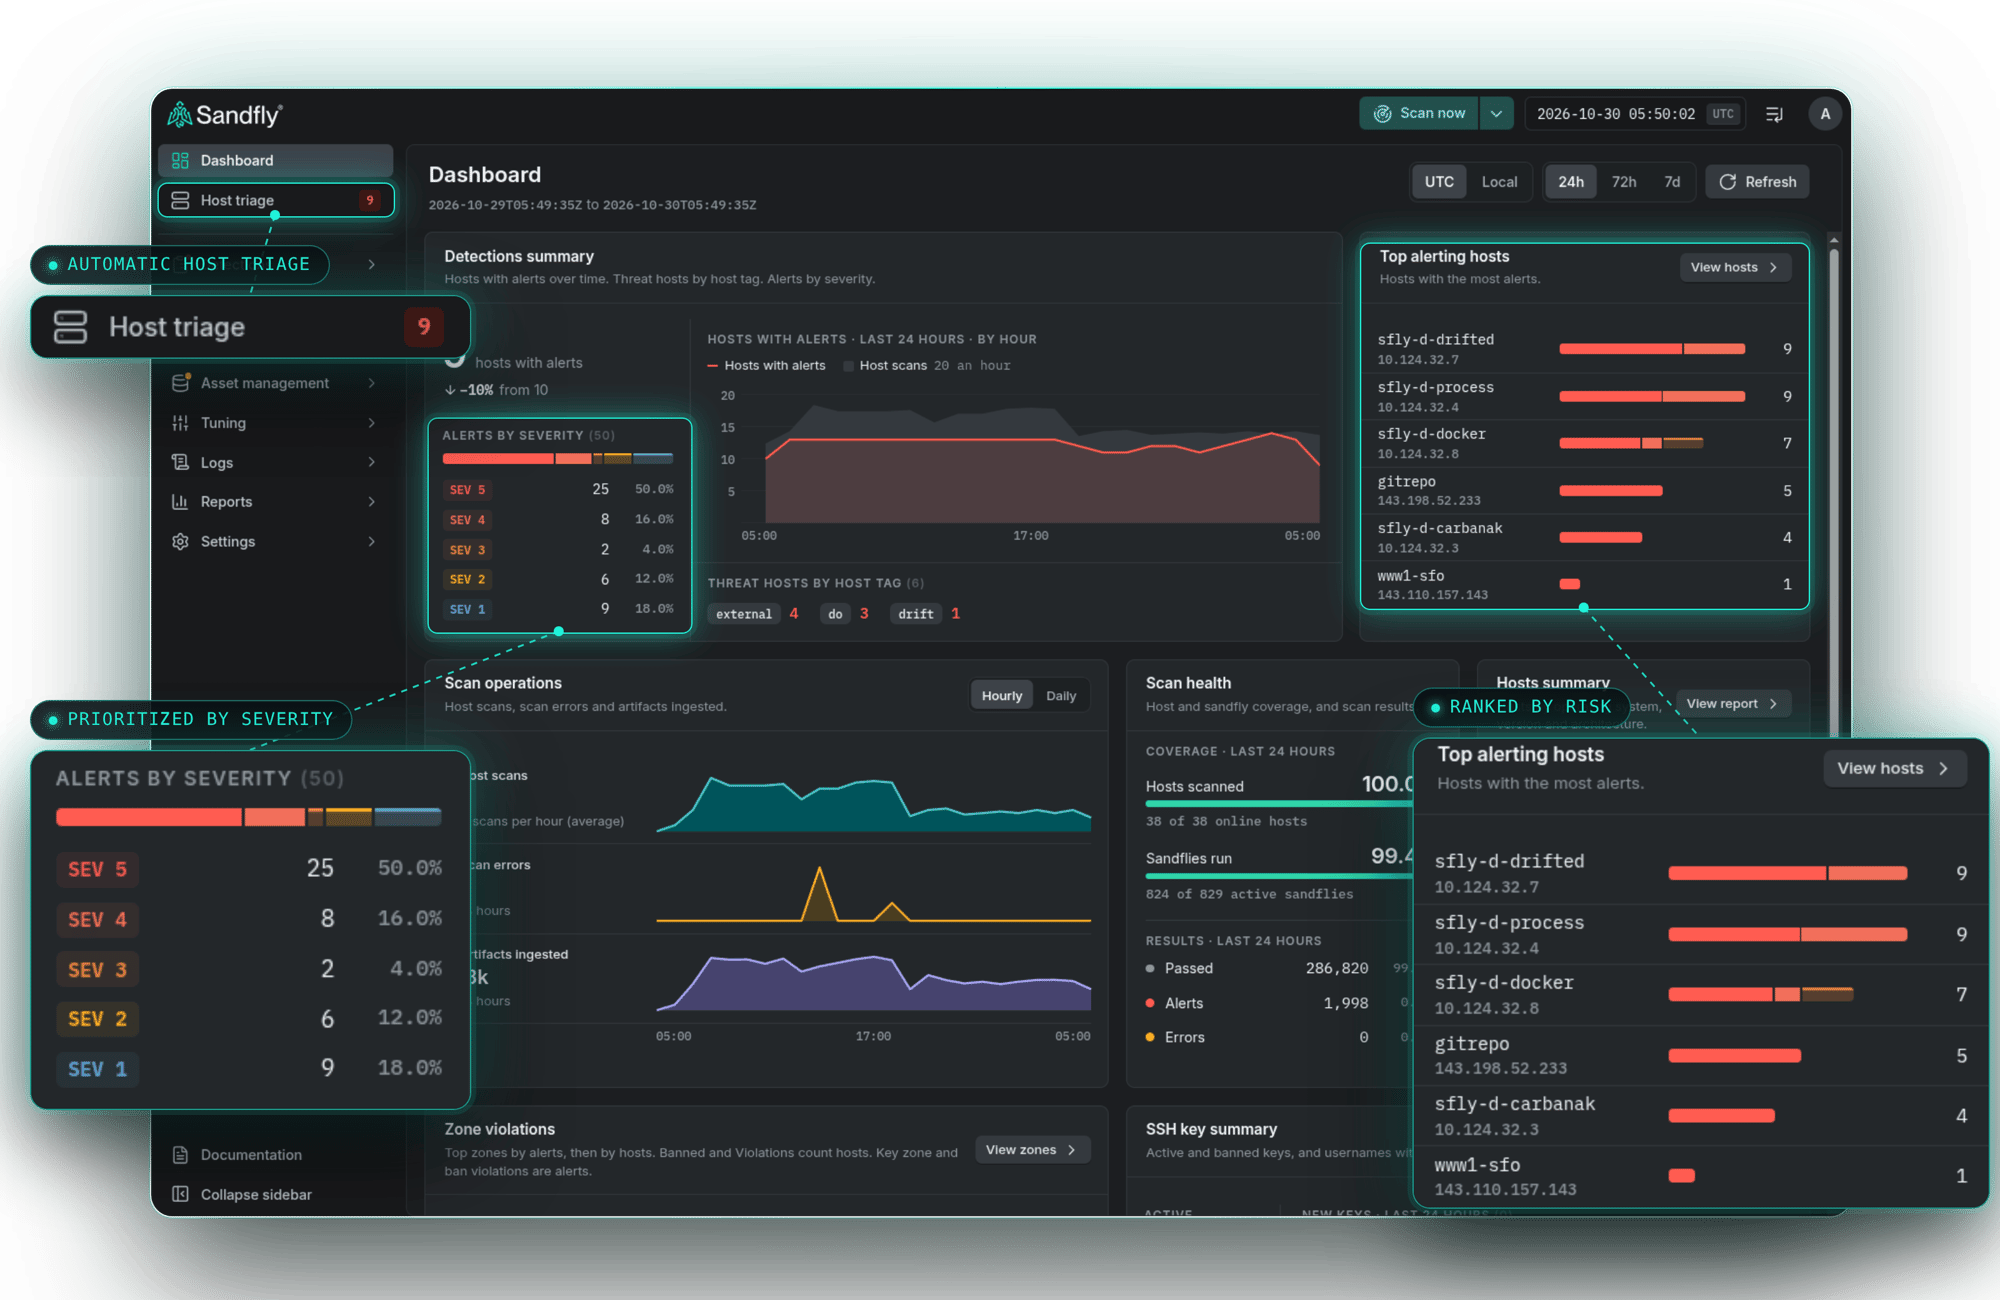
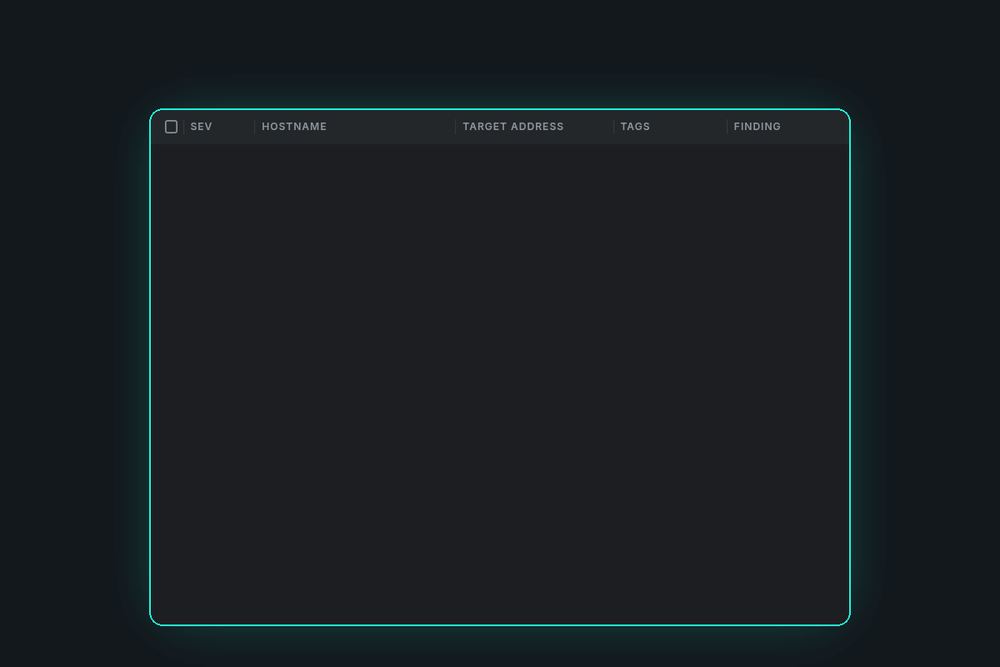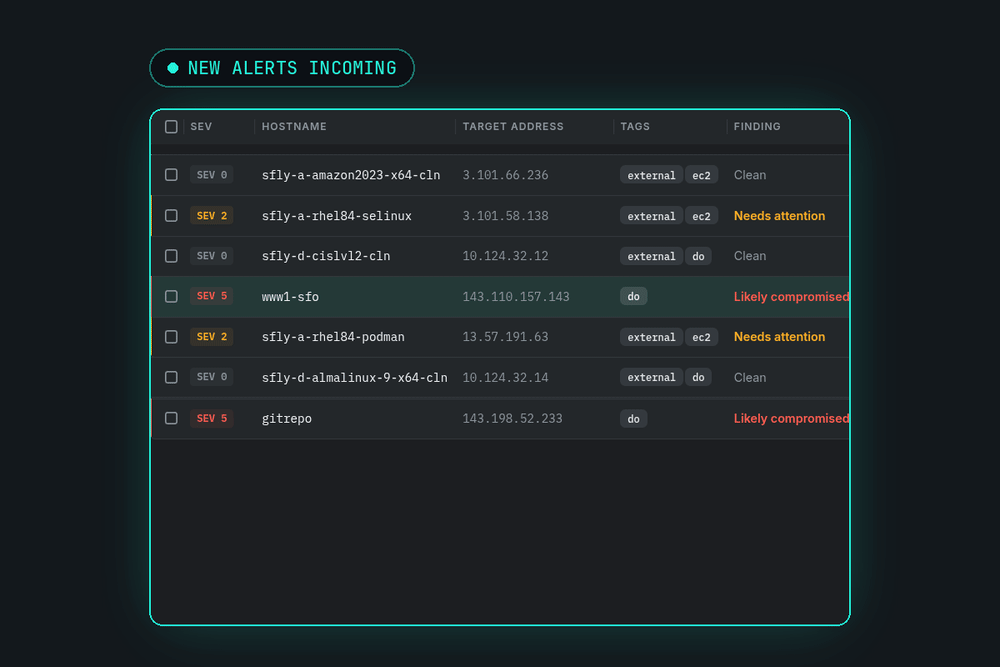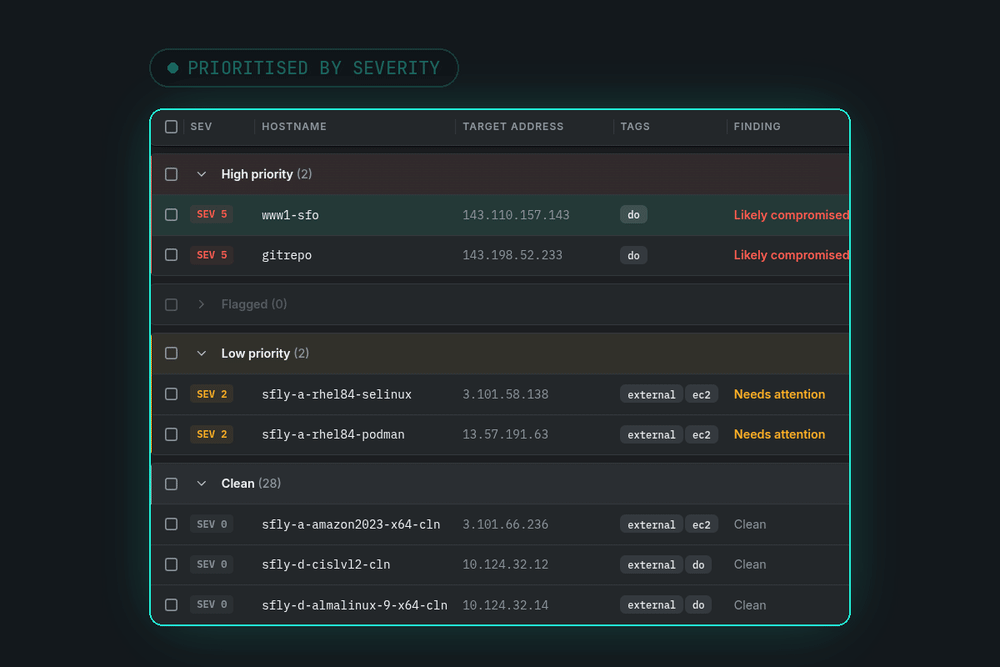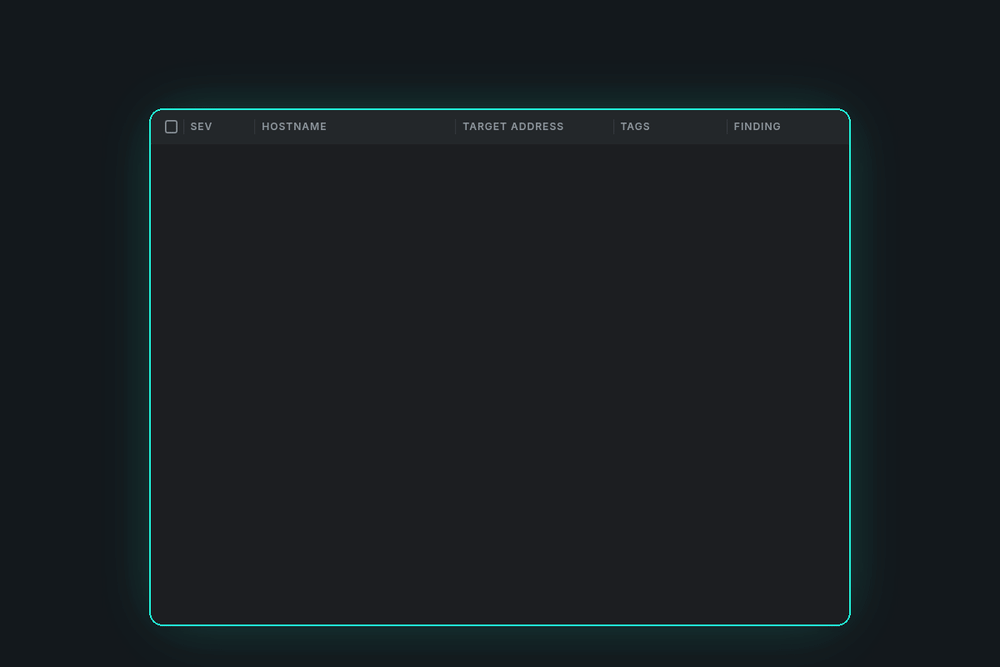
Faster triage, accurate prioritization machine learning and optional AI. Your team starts the day with a ranked list of real Linux threats, not a queue of maybes.
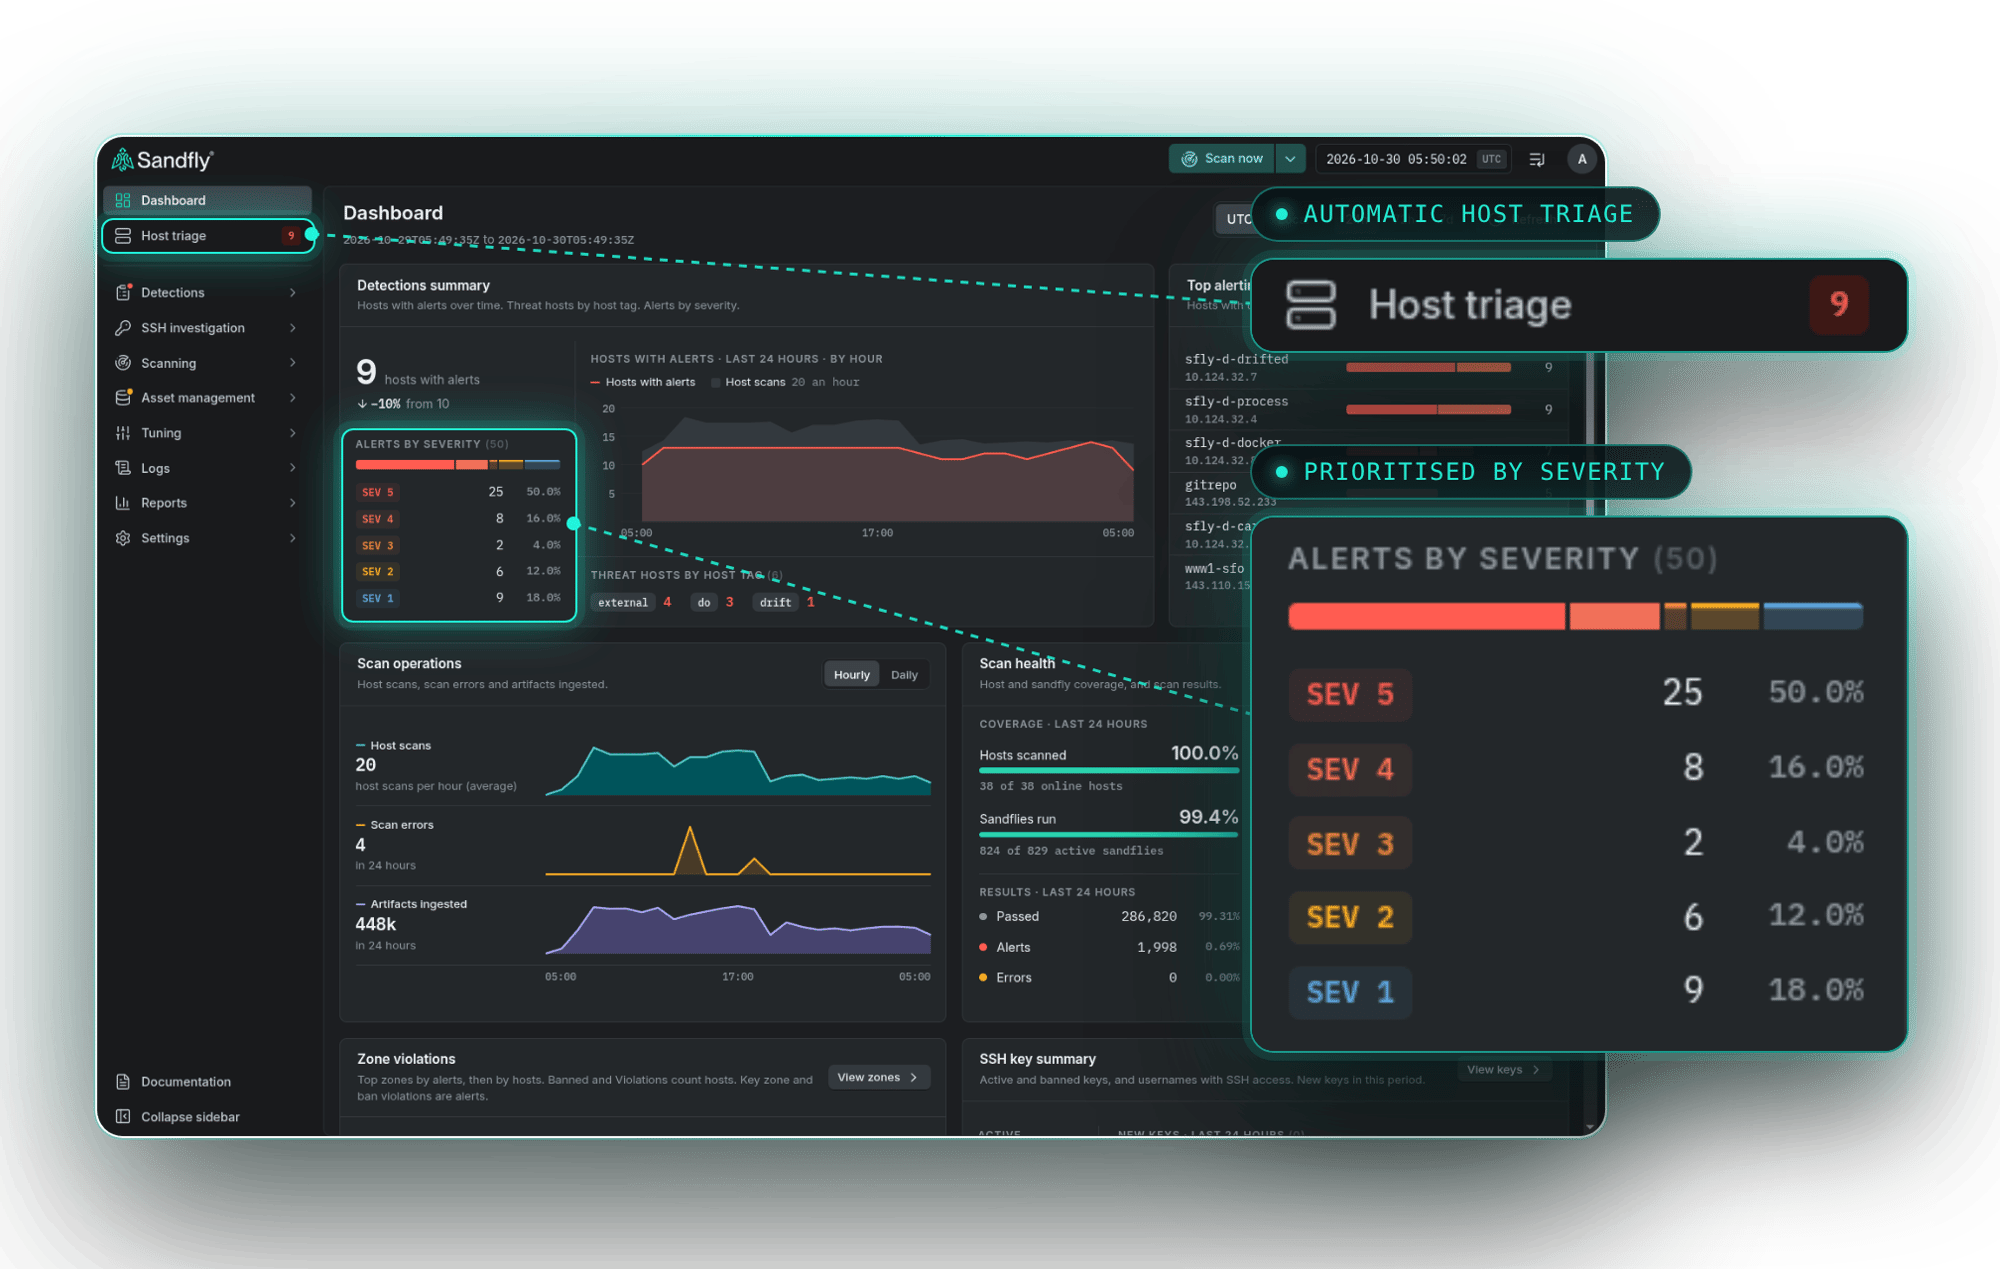
Get a high level overview of the main elements that keep operational status visible on the main screen, including:
Detection summary
Top alerts
Scanning operations and health
Zone violations
SSH keys summary
The dashboard
Get a high level overview of the main elements that keep operational status visible on the main screen including;
Detection summary
Top alerts
Scanning operations and health
Zone violations
SSH keys summary
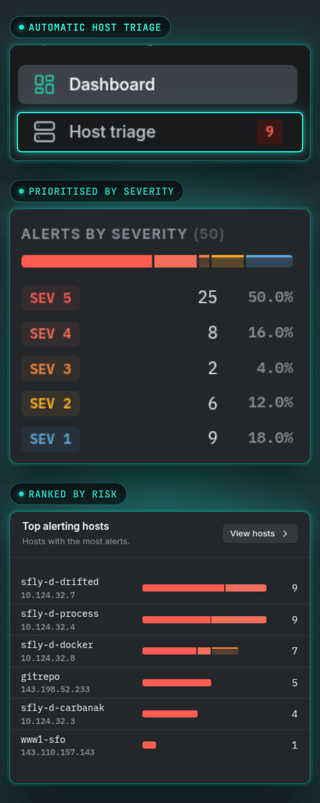
Host Triage that ranks what's real
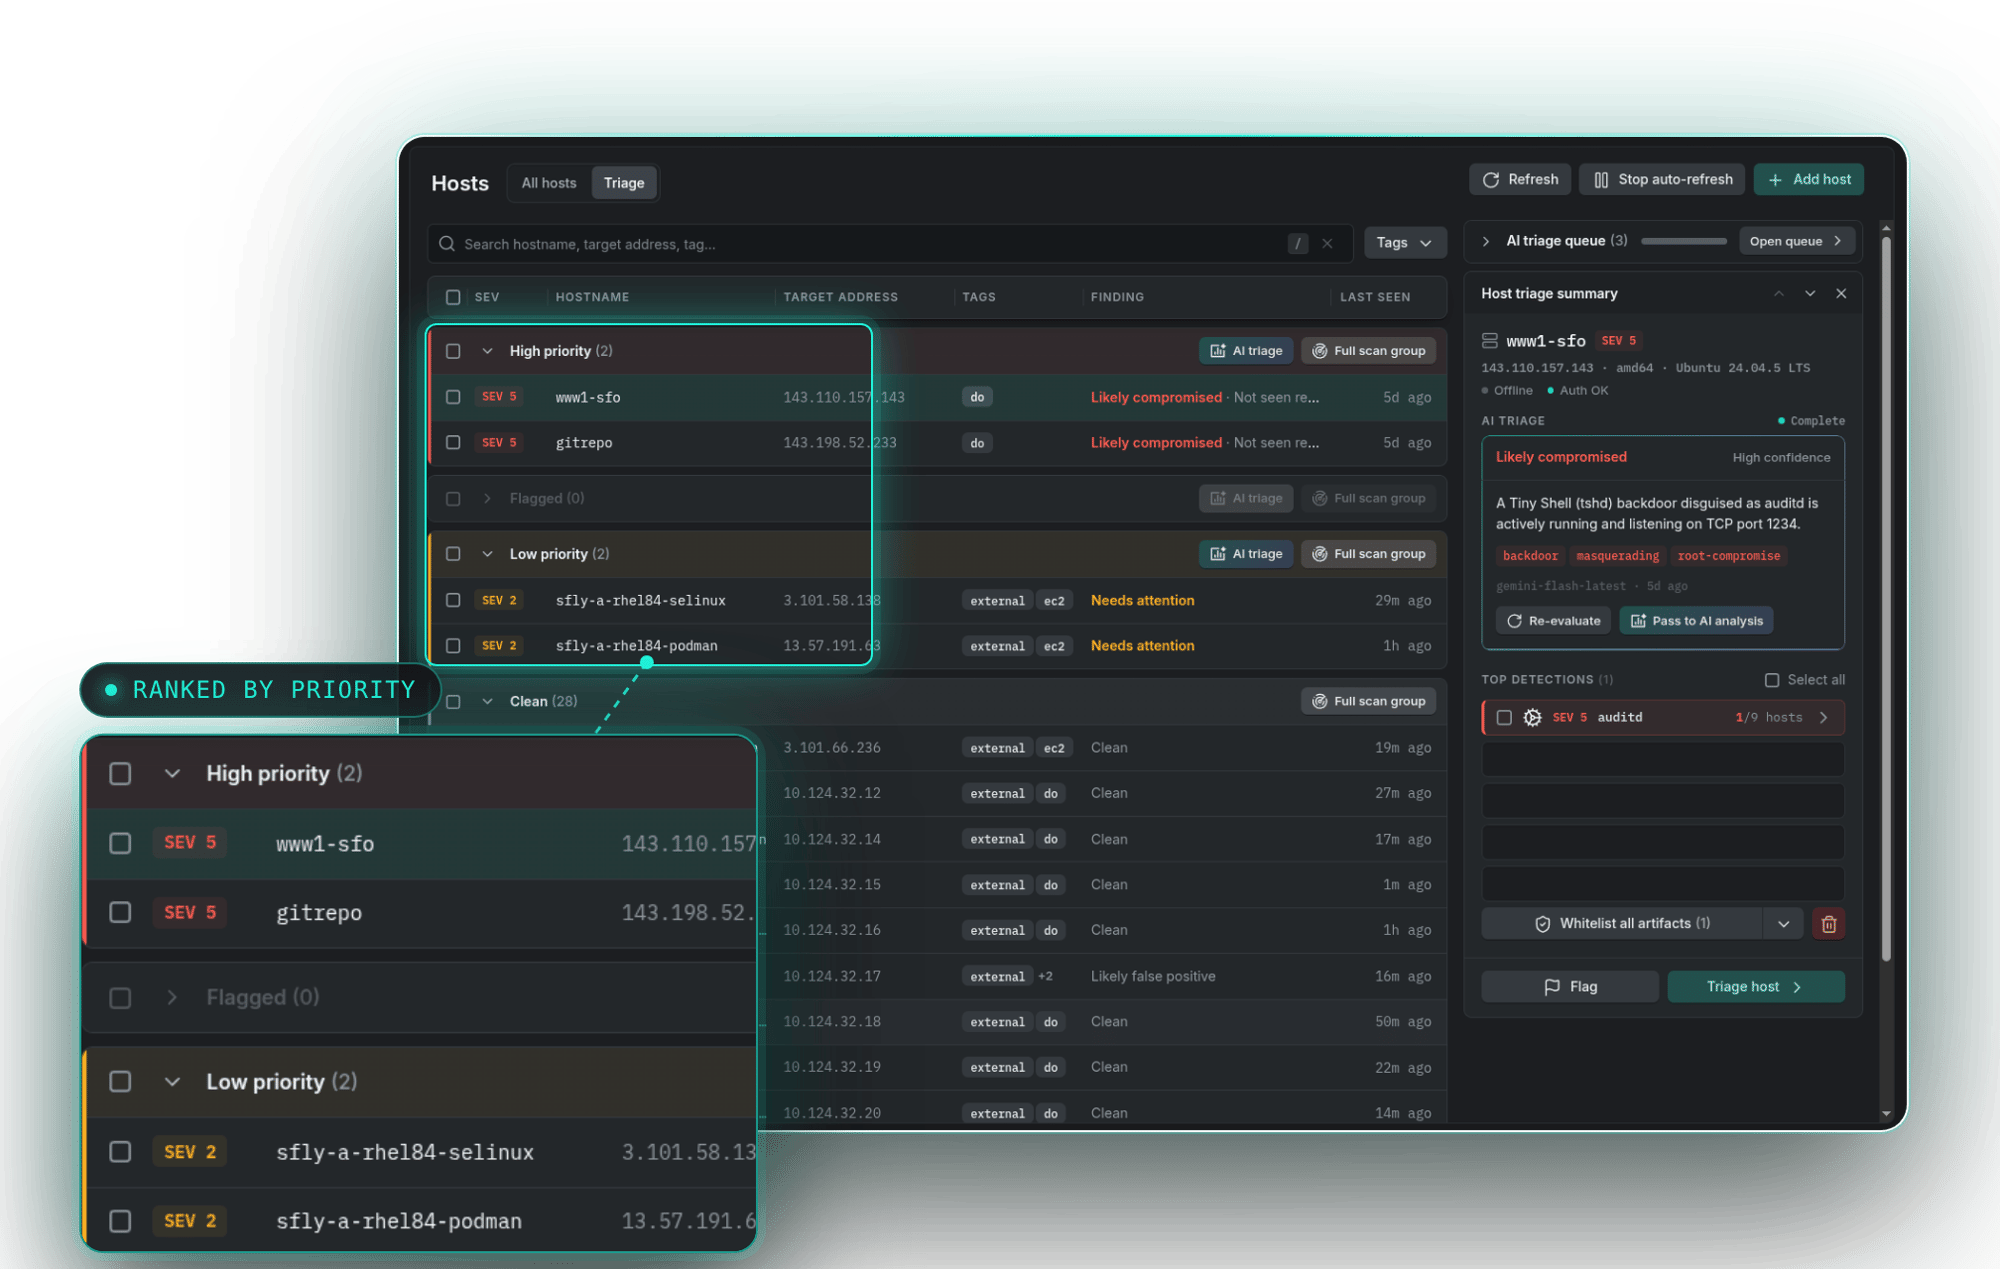
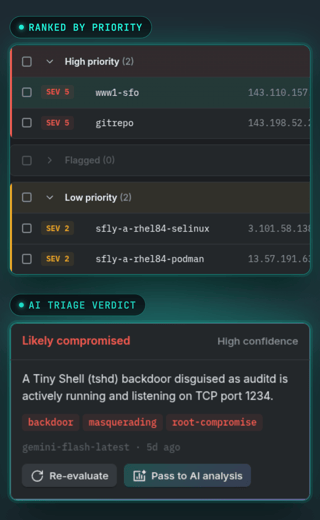
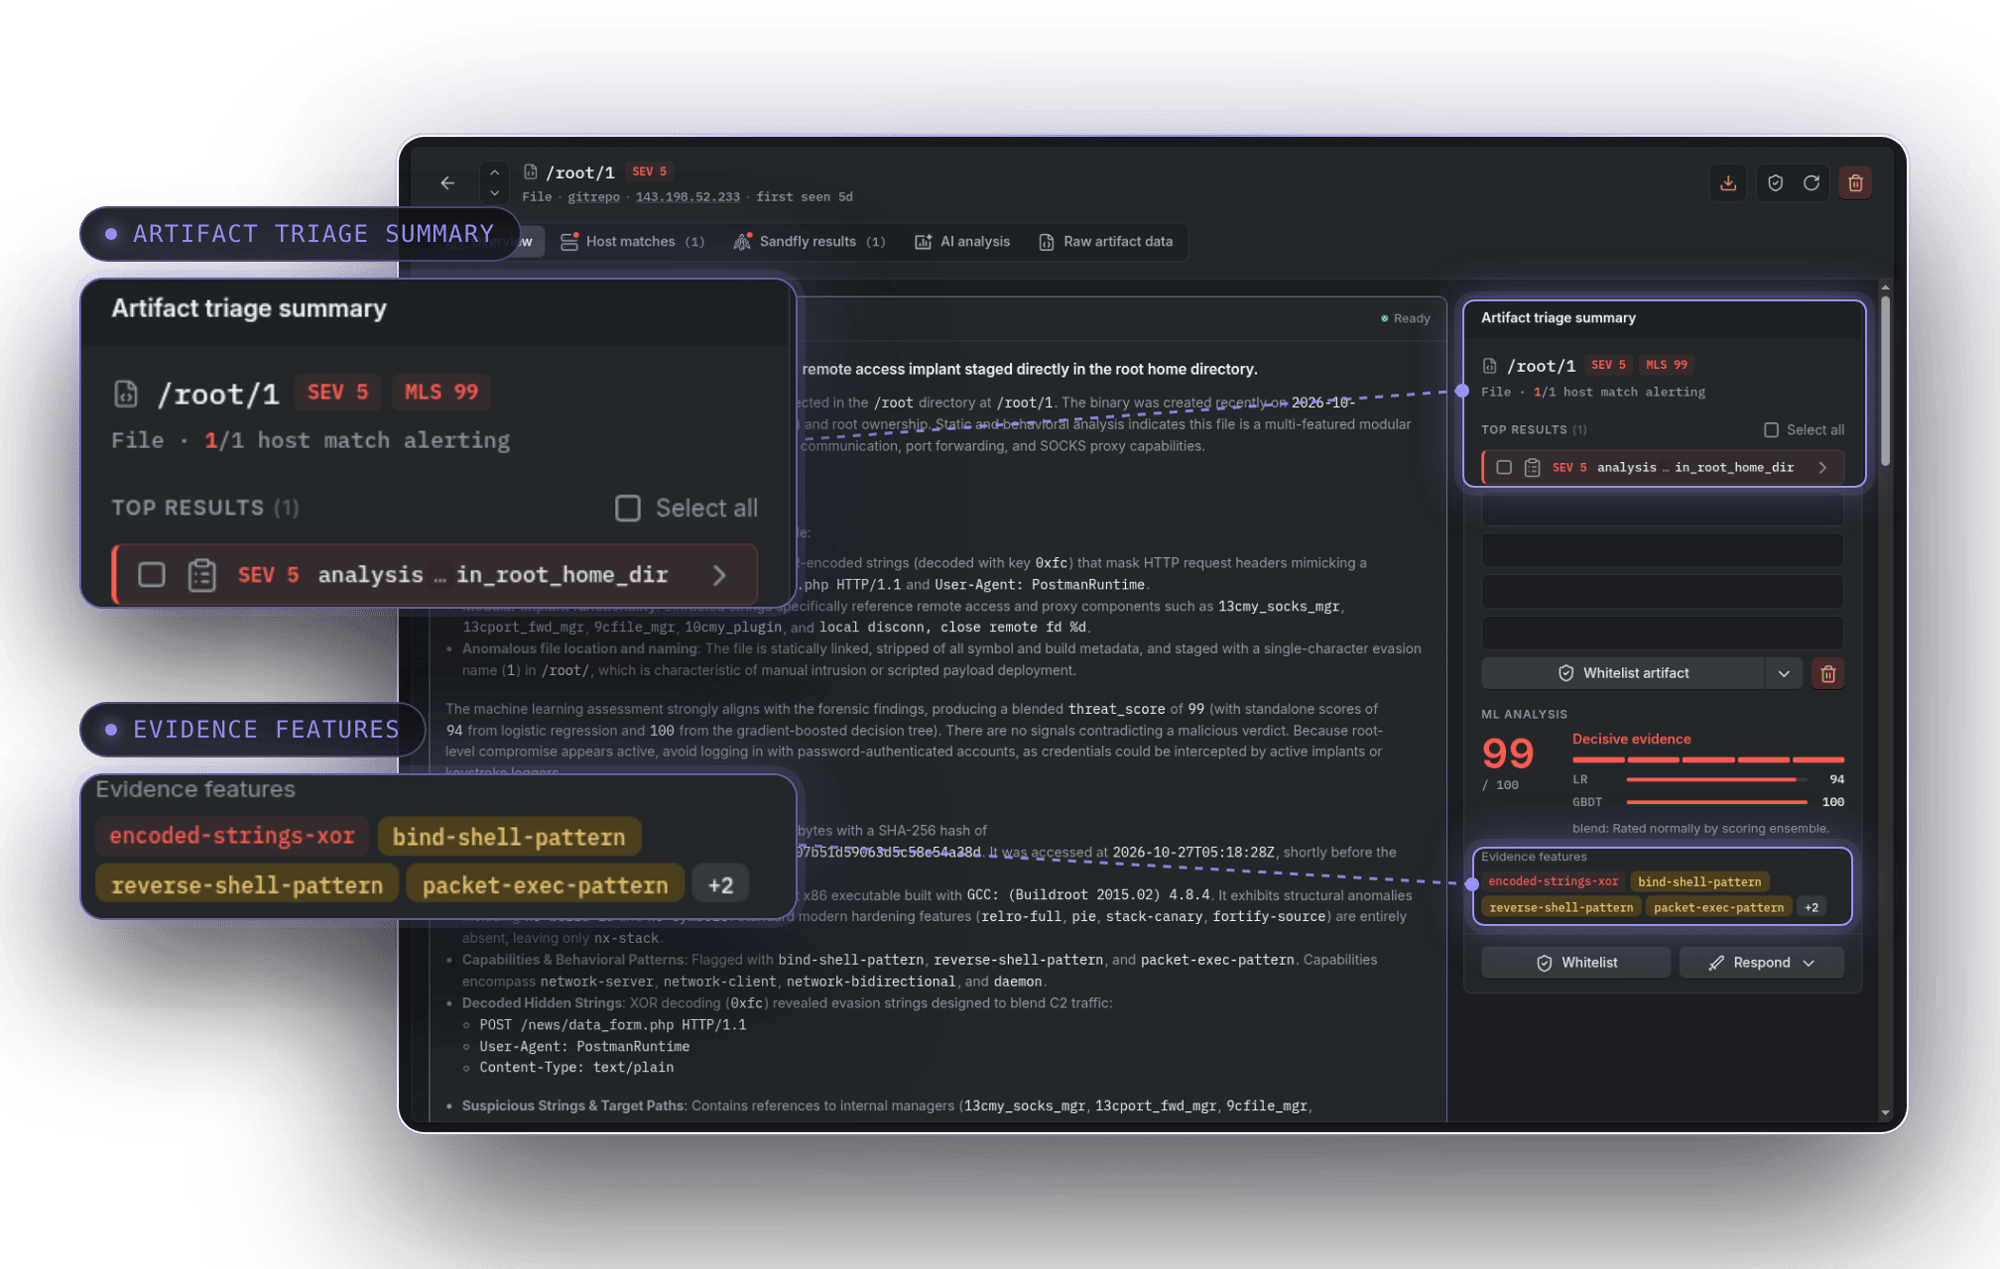
The triage summary displays an alert on the host and groups what it finds as artifacts which are ranked by priority. These are grouped and displayed clearly for further analysis.
Highest risks made easy to identify
Alerts on the host are bundled under artifacts, keeping evidence in one place
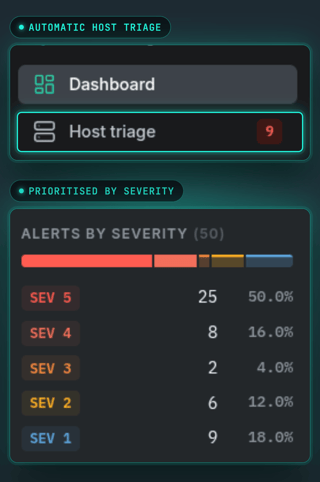
Host Triage that ranks what's real
The triage summary displays an alert on the host and groups what it finds as artifacts which are ranked by priority. These are grouped and displayed clearly for further analysis.
Highest risks made easy identify
Alerts on the host are bundled under artifacts, keeping evidence in one place
Machine learning that catches new implants
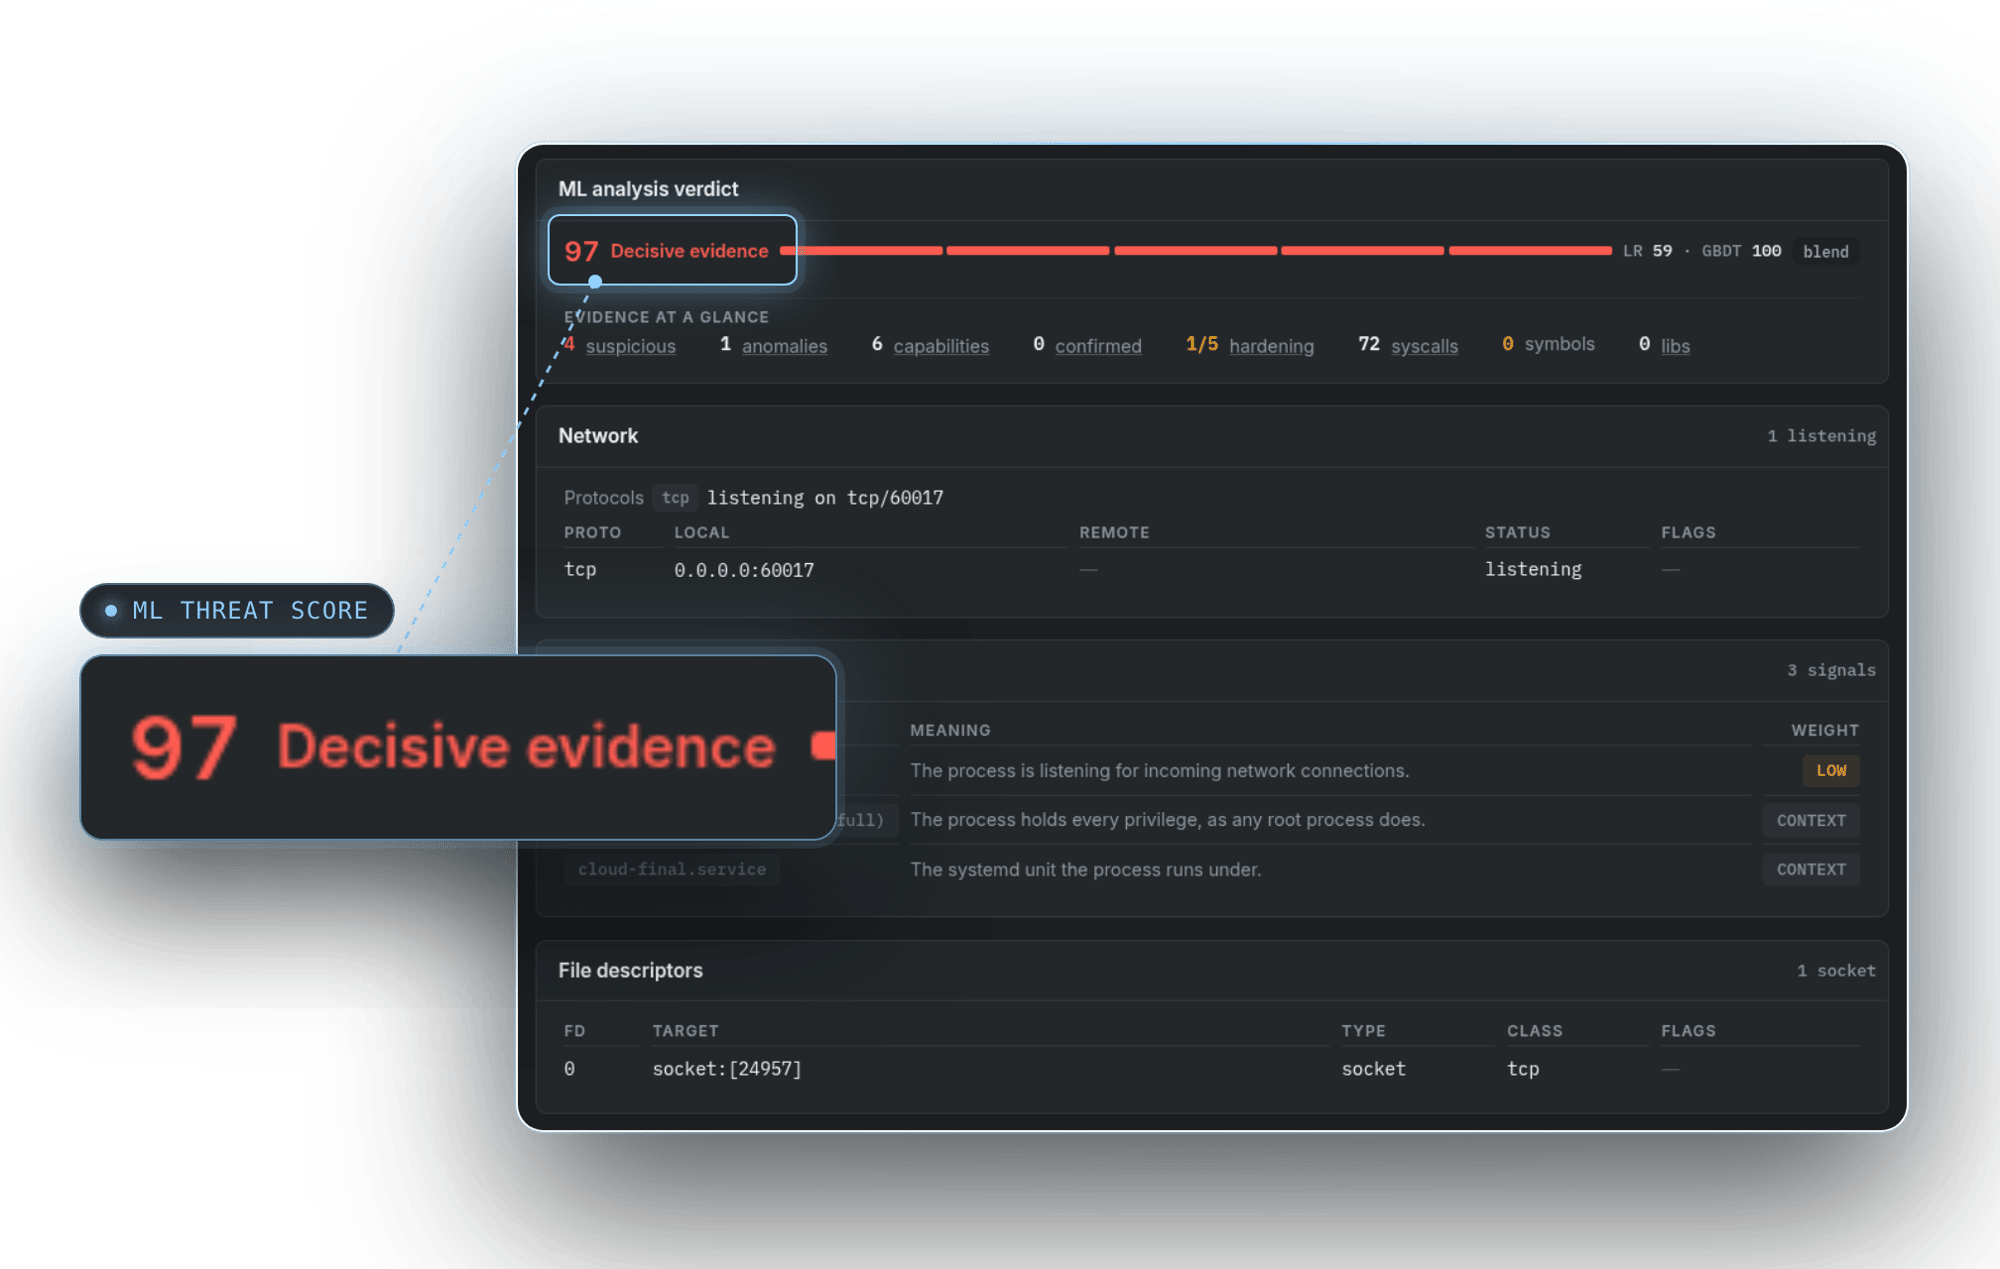
Sandfly’s machine-learning classifier hunts for Linux implants active on the system or lying in wait on the disk, including ones no one has seen before. Every binary gets a threat score that feeds straight into its severity rating.
Finds known and brand-new network implants
Works on all architectures with no performance impacts (really).
Runs agentlessly, with nothing installed on your hosts
Machine learning that catches new implants
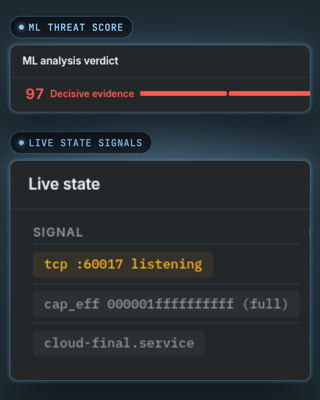
Sandfly’s machine-learning classifier hunts for Linux implants active on the system or lying in wait on the disk, including ones no one has seen before. Every binary gets a threat score that feeds straight into its severity rating.
Finds known and brand-new network implants
Works on all architectures with no performance impacts (really).
Runs agentlessly, with nothing installed on your hosts
Automated AI Triage, Lightweight
Connect any AI model and Sandfly will triage all alerts to escalate or clear threats in real time, and in plain English. Prefer to keep AI out? Everything else works without it.
Triage on all inbound alerts to prioritize what’s important.
Uses Sandfly’s high quality data for accuracy and reliability.
Optional: off by default and you can bring your own model from the cloud or on-prem.
Automated AI Triage, Lightweight
Connect any AI model and Sandfly will triage all alerts to escalate or clear threats in realtime, and in plain English.. Prefer to keep AI out? Everything else works without it.
Triage on all inbound alerts to prioritize what’s important.
Uses Sandfly’s high quality data for accuracy and reliability.
Optional: off by default and you can bring your own model from the cloud or on-prem.
Automated AI analysis witha deep dive
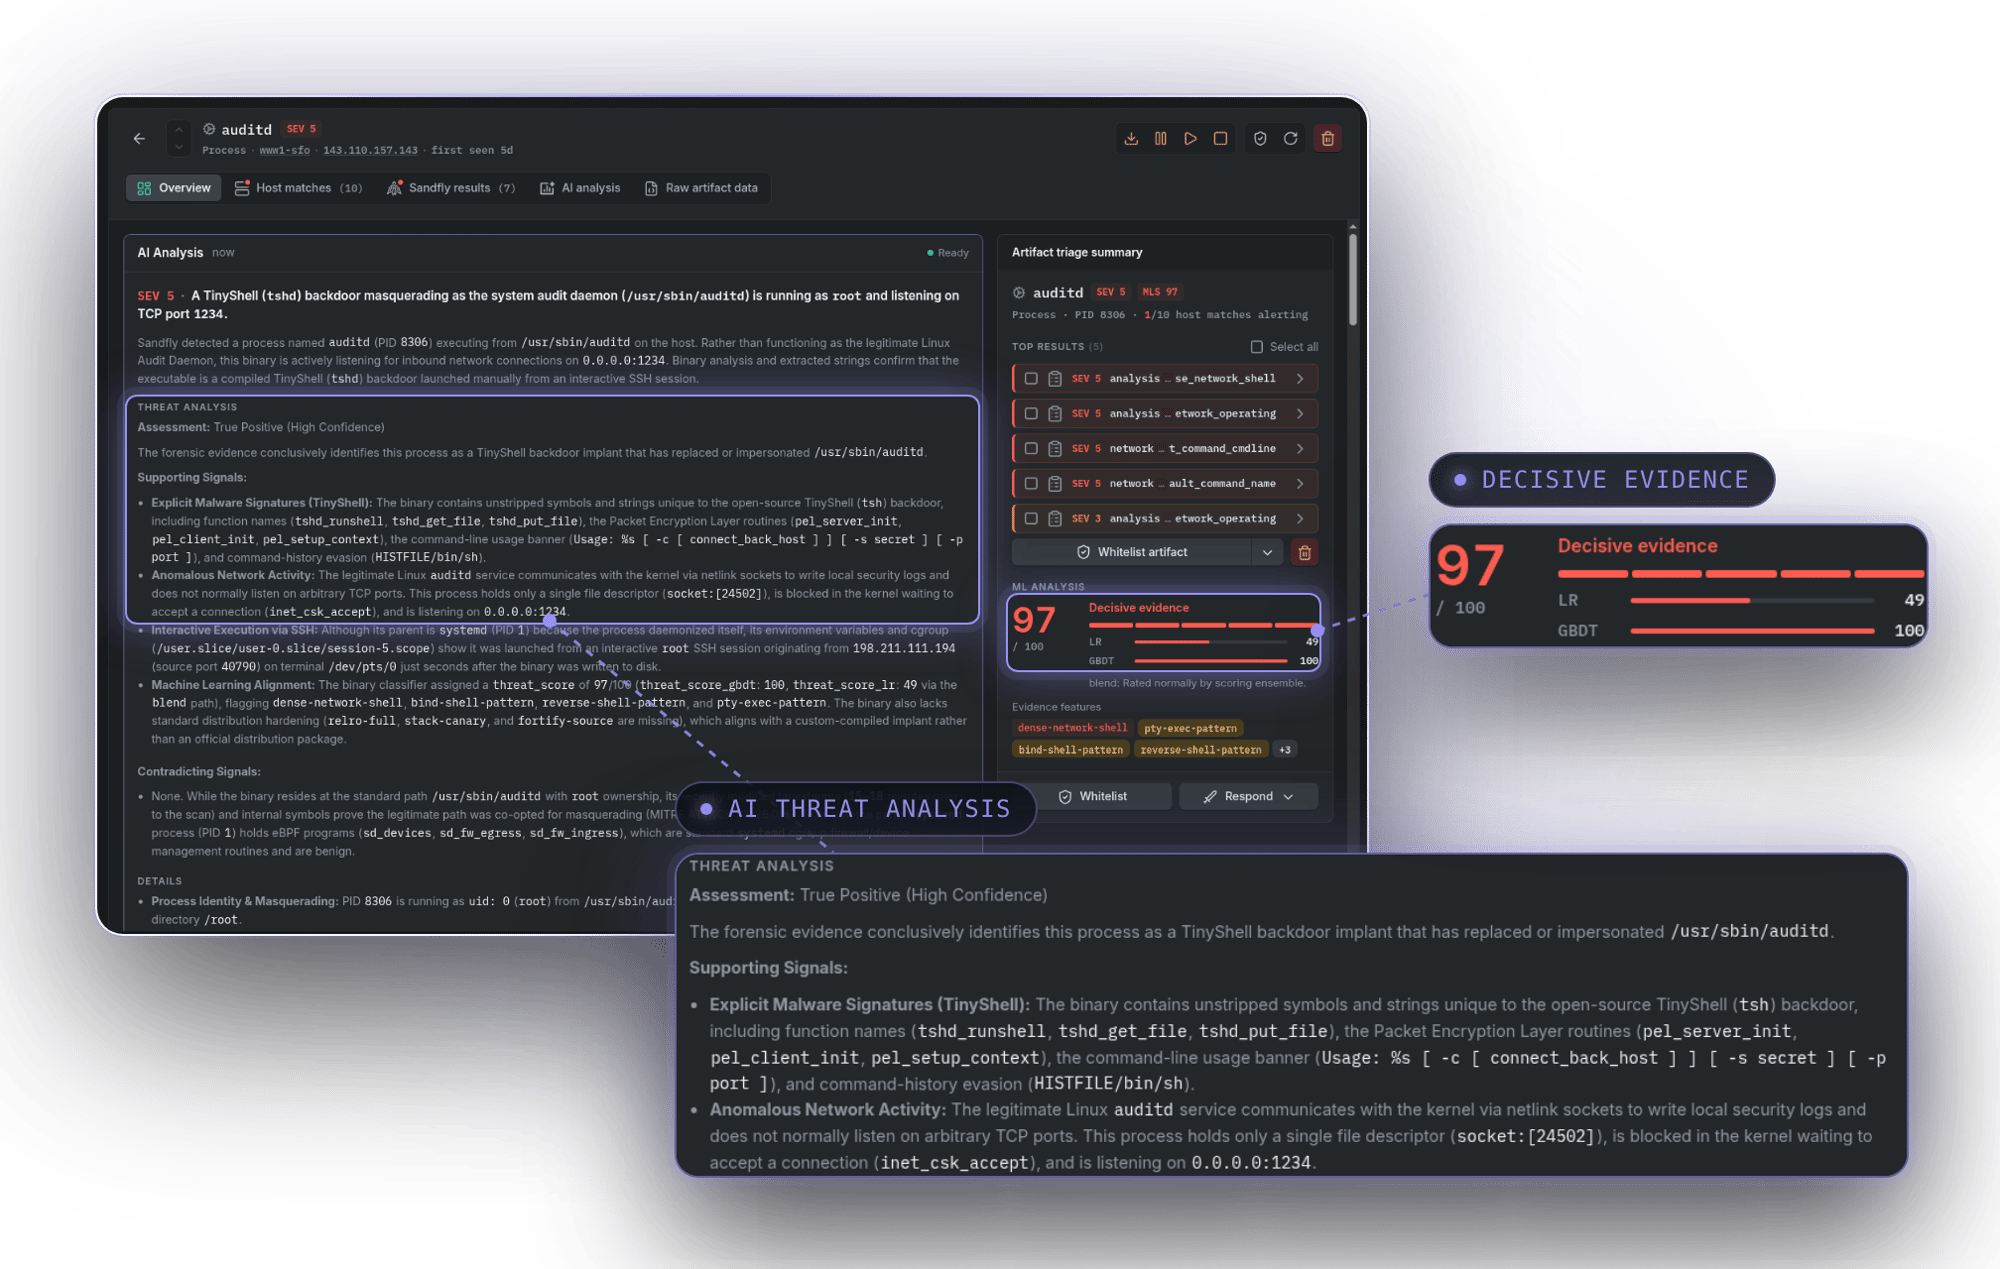
Based on the initial triage the deeper AI analysis lays out the overview with threat analytics with a full breakdown of details with it. All optional features.
String obfuscation, defense evasion, embedded backdoor along with machine learning alignment to bolster reliable insights.
Automated AI analysis witha deep dive
Based on the initial triage the deeper AI analysis lays out the overview with threat analytics with a full breakdown of details with it. All optional features.
String obfuscation, defence evasion, embedded backdoor along with Machine learning aligment to bolster reliable insights.
Read the full 6.0 story
Severity scoring, prioritization, artifact views and optional AI triage.
Blog Post
What's new in Sandfly 6.0
Every change in the release, what it means for your team and how to get started
No. Every feature works without it, and the AI summaries are optional.
Customers can bring their own model or use a commercial offering. Sandfly also supports on-prem models using industry standard OpenAI API calls.
6.0 is lighter on your systems, not heavier. The scanning engine has been optimized to reduce the load on the hosts being scanned. In fact, 6.0 is as fast or faster than all previous versions of Sandfly.
No agents, just SSH. This reinforces your main differentiator.
The ML malware classifier is designed to hunt for Linux implants, which represent a significant threat to enterprise and critical infrastructure. It runs agentlessly and profiles binaries in a couple milliseconds with no performance impacts across all supported architectures, including embedded devices and custom Linux distributions.
Every Linux host checked. Nothing installed.
No agents, no kernel modules, nothing left behind. See how Sandfly hunts for intruders across your environment without touching production.