Full security visibility on Linux, zero footprint.
Sandfly connects over SSH, hunts for intruders and malware around the clock, and gathers the forensic evidence your team needs to act.
-
Nothing installed. No agent, no kernel modules, no syscall hooks. Sandfly connects over SSH and leaves nothing behind.
-
Deployed in minutes. Scanning your first hosts the same day, not after a rollout project.
-
Works everywhere. Almost any distribution, from decade-old systems to modern cloud.
We needed visibility into the systems, but it also could not impact production. We could not be toppling servers, we could not be causing production issues. Sandfly proved that it would not cause problems in evaluation, and it has held up in production.
-Senior Security Engineer, automotive manufacturer
Talk to an Expert
THE CONSOLE
Comprehensive Linux Security
Sandfly's deep understanding of Linux intruder tactics offers reliable and effective threat protection. Known and unknown attacks are detected safely and fast.
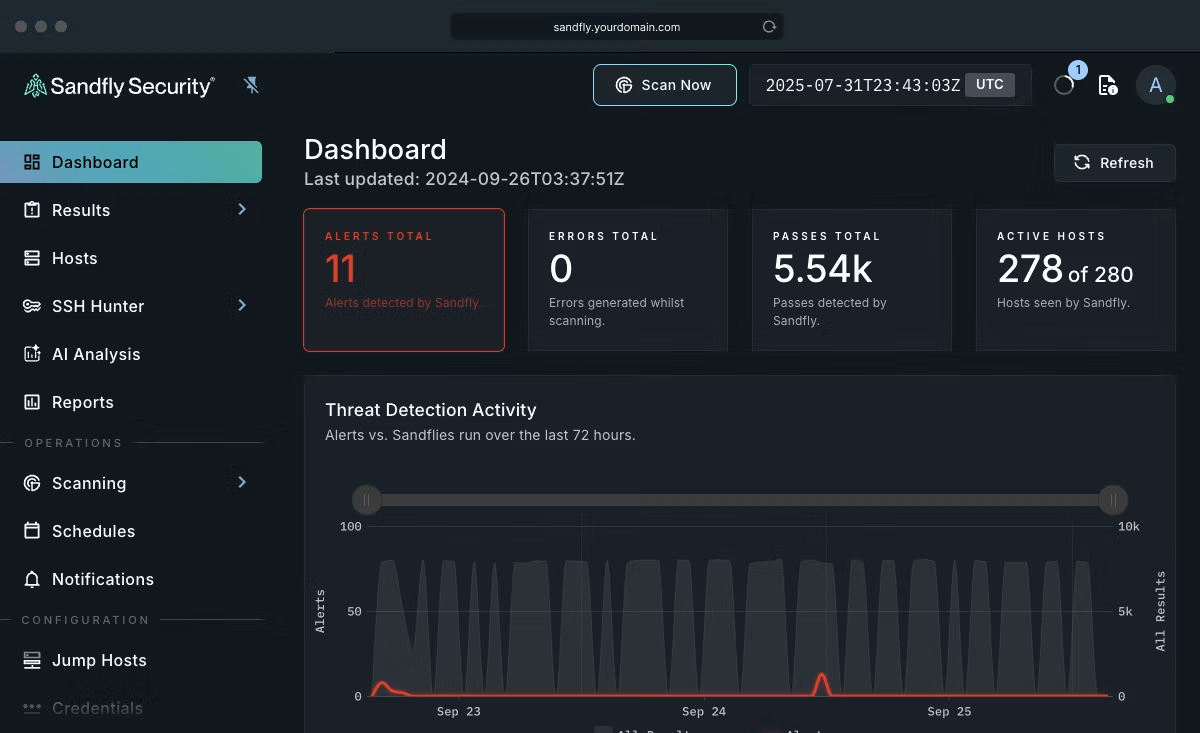
How Sandfly works
Yes. There is no agent to install on your Linux hosts. Sandfly only needs SSH running on them, so there is nothing to deploy or maintain on each endpoint.
Virtually all of them. Sandfly covers the widest range of Linux on the market, from systems over ten years old to modern cloud, across Intel, AMD, Arm, MIPS and IBM Power.
Sandfly uses a server and node design. You add nodes to cover different network segments, and reach isolated networks through jump or proxy hosts.
It hunts for intruders, malware and suspicious activity on Linux 24 hours a day, gathers forensic evidence, and can run automated responses once a threat is found.
Contact Us
General Navigation
Get Blog updates
© 2026
© 2026 Sandfly Security, Ltd. End User License Agreement & Privacy Policy. This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply. Linux® is the registered trademark of Linus Torvalds in the U.S. and other countries.