Skip to the main content.

Find what's hiding on your Linux systems

Full access to Sandfly, FREE for 14 days.

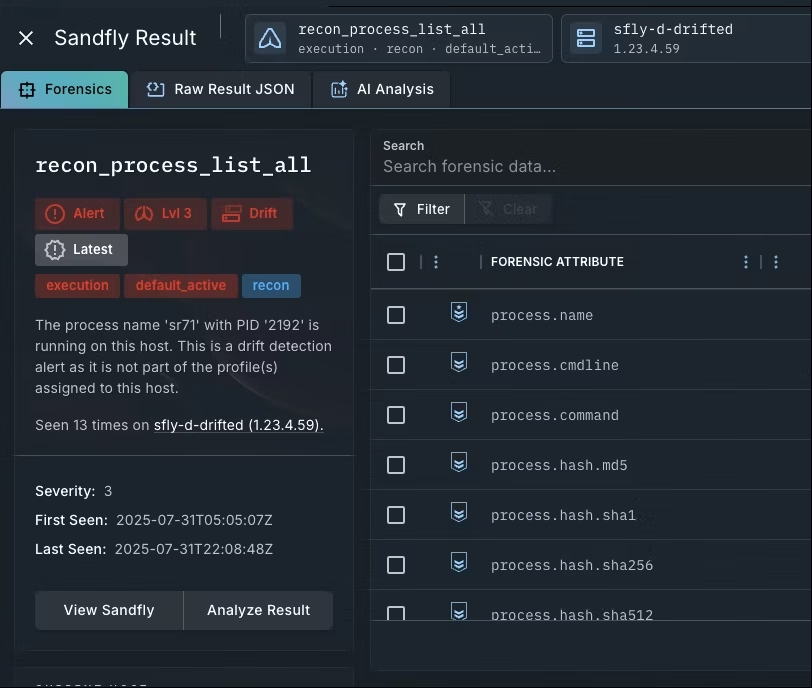
Attackers hide in plain sight on Linux, fake processes, tampered binaries, rogue SSH keys. Sandfly finds them.

Nothing to install and no sales call. Sandfly works over SSH, so most people are up and scanning quickly.

Licence within one business day. No sales call required.

product-image-sandfly-results-crop
1771363141-carahsoft-white-logo-sandfly-security-partner 1771939095-cyberteam360-logo-white image logo-digital-ocean logo-sorasec

What to expect

We'll review your request

We will issue you a trial license within one business day. There's no sales call required.

You get your licence and guide

Your licence arrives with the install guide. Sandfly runs in Docker on a Linux VM you control, most teams are up in under 30 minutes.

Connect your hosts and scan

Point Sandfly at your Linux environment over SSH and run your first scan. Nothing gets installed on the hosts themselves. 

Before you start

Return to top