Skip to the main content.

Find what's hiding on your Linux systems

Sandfly 14-Day Free Trial

Attackers hide in plain sight on Linux, fake processes, tampered binaries, rogue SSH keys. Sandfly finds them.

Nothing installed on your hosts and no sales call. Sandfly works over SSH, so most people are up and scanning quickly.


No credit card required.

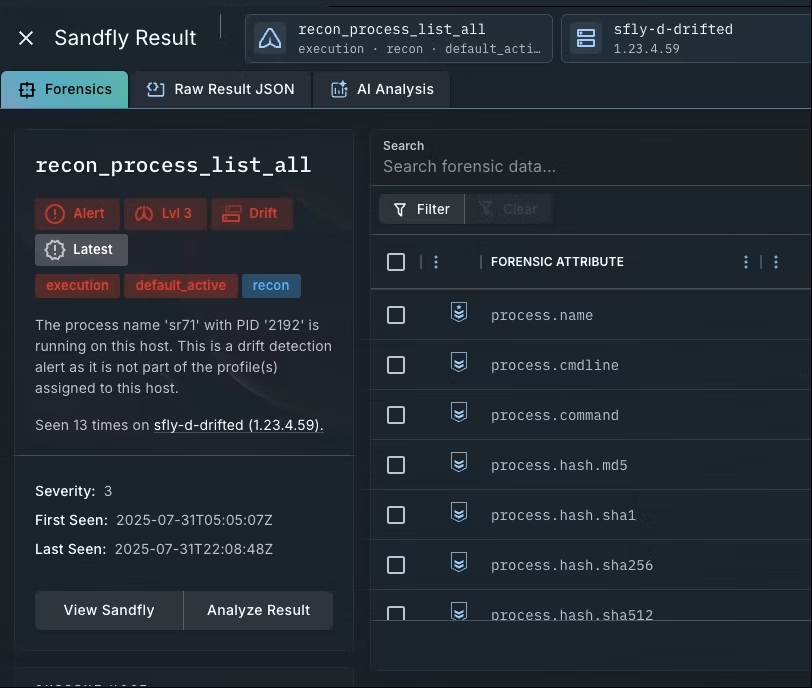
Sandfly dashboard showing a drift detection alert for a suspicious Linux process, with forensic details like process name and hashes


"We can't compromise on either security or stability when lives are at stake."

Edgar Avetisyan, Senior Security Engineer, Vay


1771363141-carahsoft-white-logo-sandfly-security-partner 1771939095-cyberteam360-logo-white image Digital-ocean-logo logo-sorasec

What to expect

We'll review your request

We will issue you a trial license within one business day. There's no sales call required.

You get your licence and guide

Your licence arrives with the install guide. Sandfly runs in Docker on a Linux VM you control, most teams are up in under 30 minutes.

Connect your hosts and scan

Point Sandfly at your Linux environment over SSH and run your first scan. Nothing gets installed on the hosts themselves. 

Before you start

Return to top