1 min read
Detecting Linux Stealth Rootkits with Directory Link Errors
Publication Date: 25 June 2024
1 min read
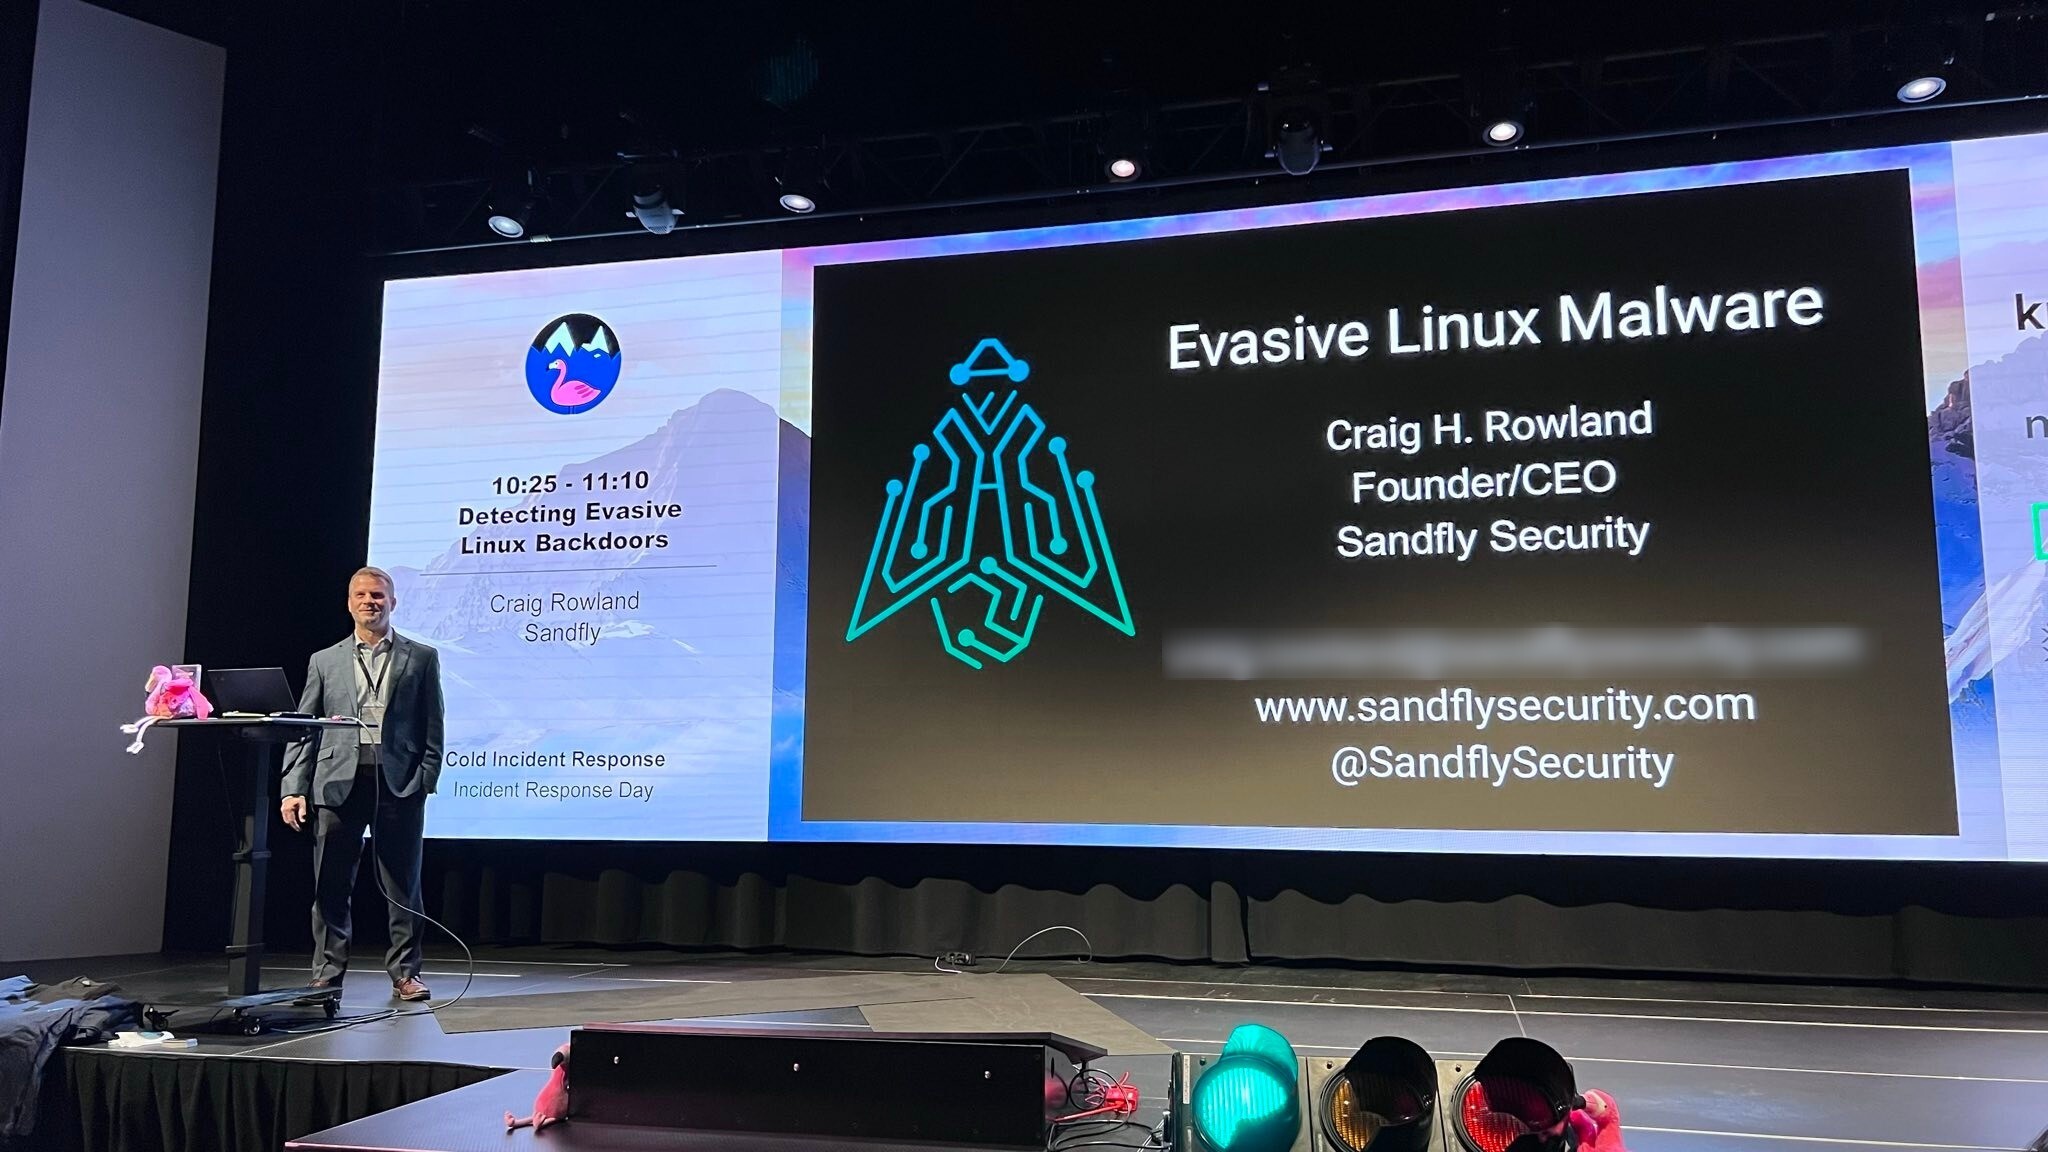
Sandfly founder Craig Rowland gave a presentation for the FIRST Cold Incident Response Conference in Oslo on evasive Linux backdoors and malware below:
Evasive Linux Backdoors and Malware Presentation
This talk focused on the infamous BPFDoor backdoor. BPFDoor used a combination of simple evasion techniques to avoid detection on Linux by doing the following:
In this presentation we go over the elements that make for effective Linux malware and how to detect them using simple command line forensics such as the following:
We thank the organizers of the conference for having us speak.
1 min read
Publication Date: 25 June 2024
1 min read
Sandfly Blog Sandfly 5.3 - Detailed Host Forensics and Microsoft Sentinel Integration 27 January 2025 Product Update
1 min read
Publication Date: 14 November 2023