





1 min read
Sandfly 2.9.0 – Protect Your Linux Hosts Free Instantly
Sandfly Blog Sandfly 2.9.0 – Protect Your Linux Hosts Free Instantly 13 April 2021 Product Update
1 min read
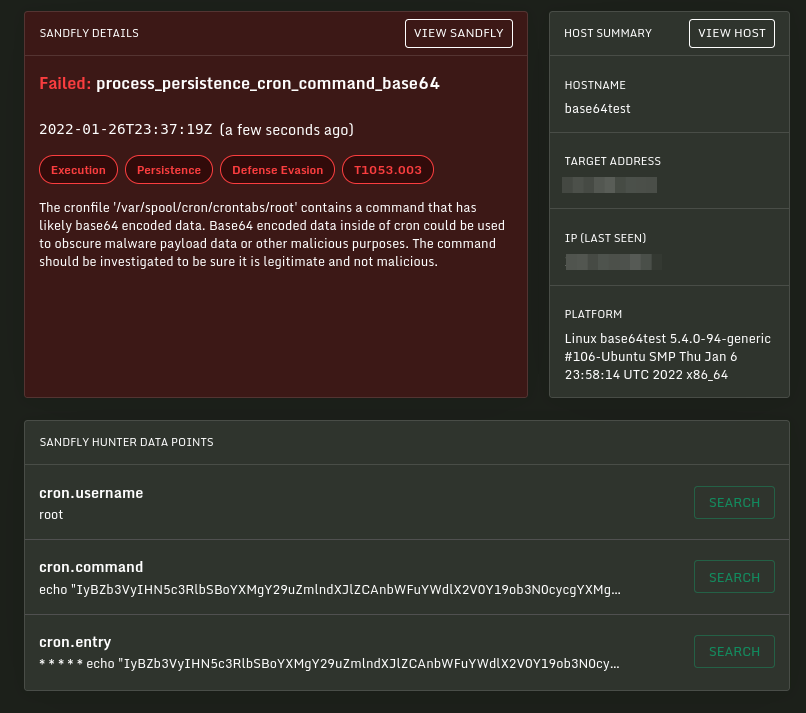
Sandfly 3.2 features new threat detection modules for suspicious base64 payloads, suspicious processes and suspicious systemd behaviors. Plus, version 3.2 has new host and alert views along with rapid view of key Linux forensic data details.
This latest release adds new sandfly checks for:
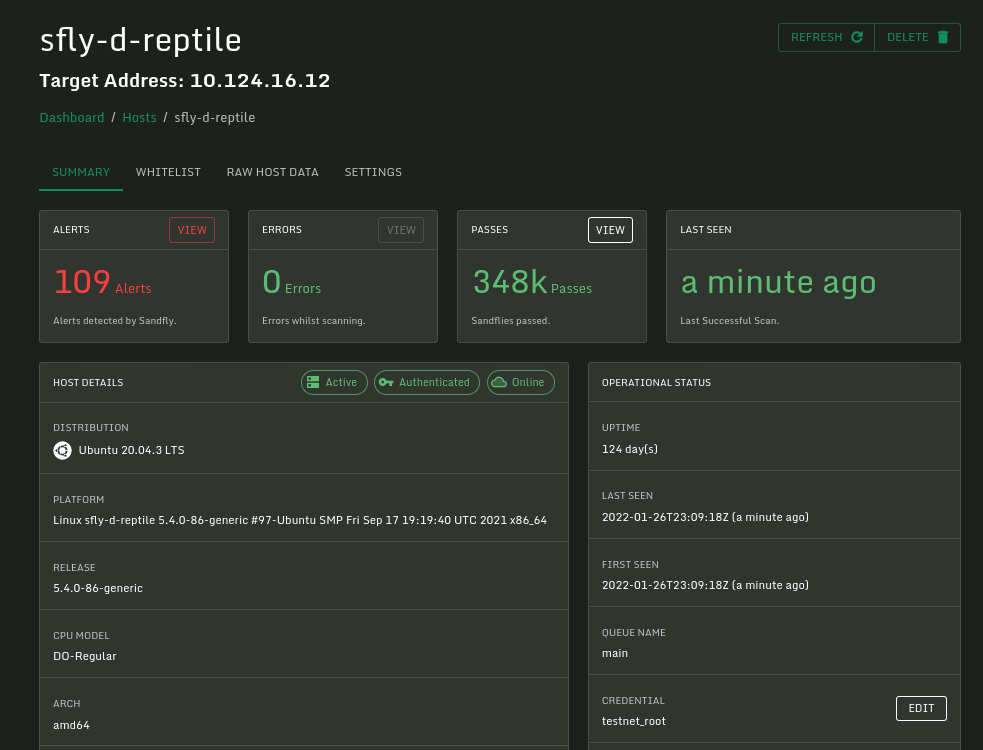
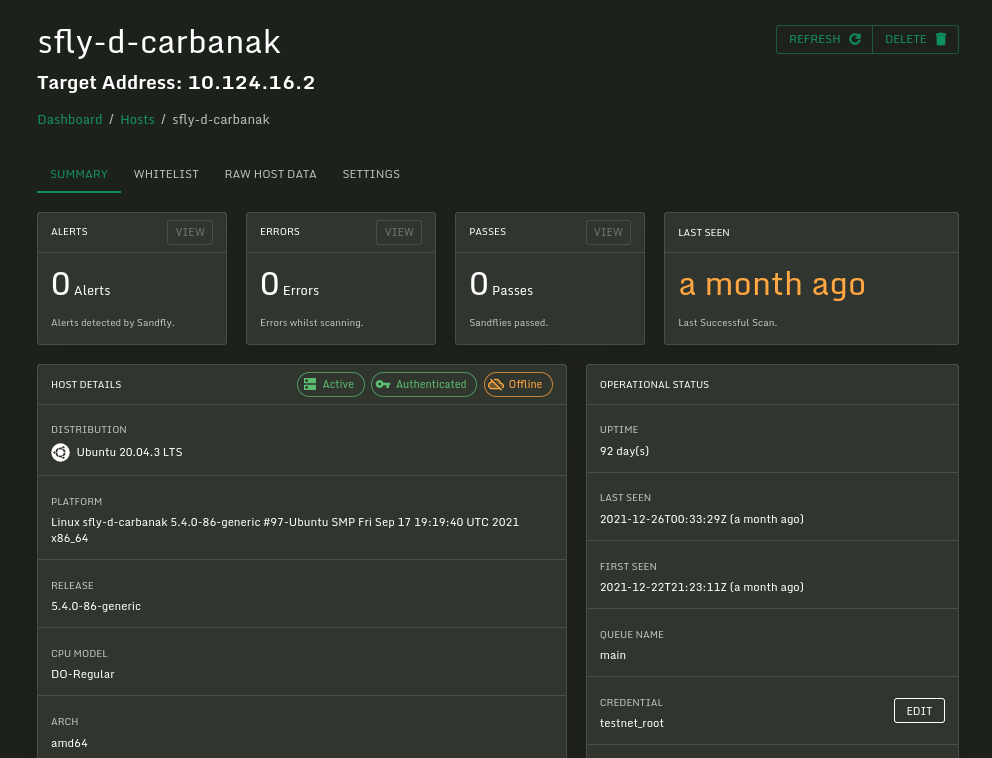
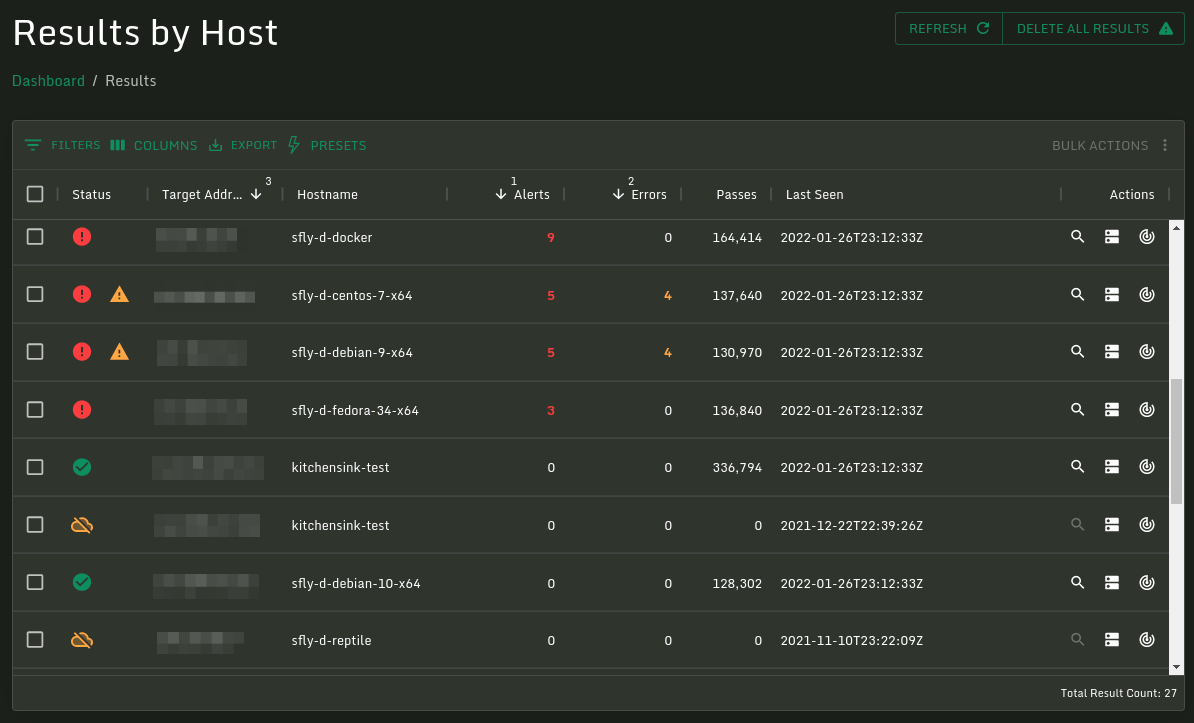
Our new offline detection feature lets you know when we haven't seen a host within 24 hours so you know it is no longer being monitored. The top bar under the host status shows time elapsed since the host was last seen with quick access to any alerts if present.
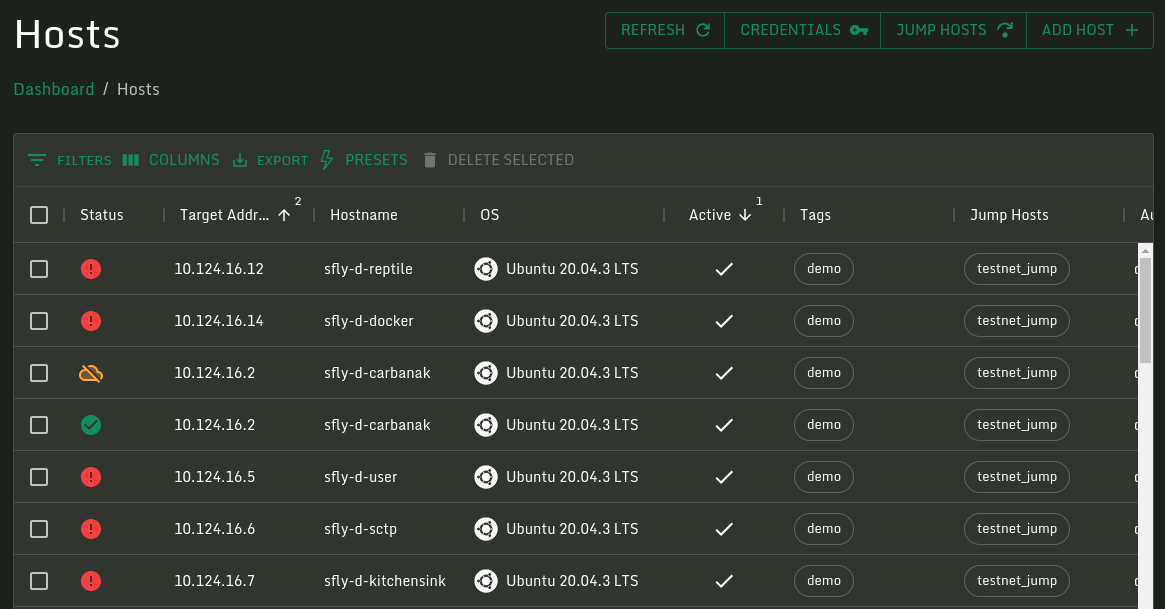
The new host alert view gives you a total alert count for all hosts and allows you to quickly explore alerts just for the affected system by a simple click.
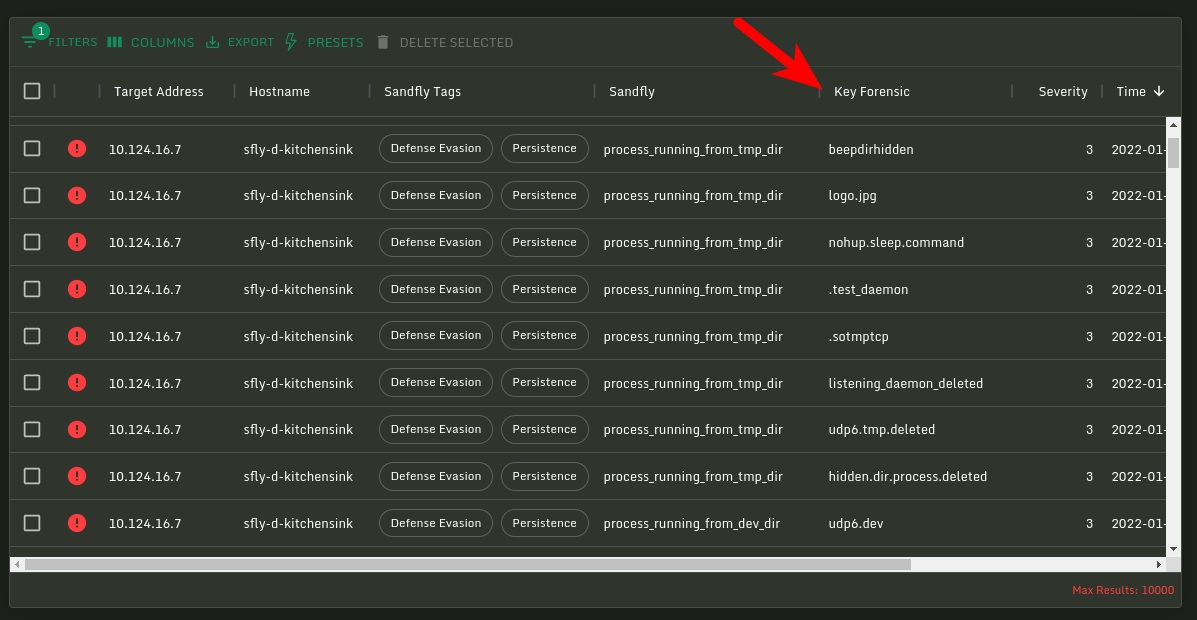
The master results list has a new column called "Key Forensic." This column shows you the primary element of the alert to help you quickly see critical forensic data. For instance, a process alert will show you the process name flagged and suspicious users will have the username shown. This allows analysts to browse their alerts and prioritize what is most important with a quick glance.
All free and paid customers can upgrade today. Please see the upgrade documentation for instructions on how to quickly and easily upgrade.
1 min read
Sandfly Blog Sandfly 2.9.0 – Protect Your Linux Hosts Free Instantly 13 April 2021 Product Update
1 min read
P ublication Date: 30 March 2026
1 min read
Publication Date: 16 June 2025