

1 min read
Linux Stealth Rootkit Process Decloaking Tool Updated
Publication Date: 21 November 2022
2 min read
Publication date: 16 August 2020
This tool was released as a response to the disclosure by the FBI and NSA of a new piece of cloaked Linux malware called “Drovorub” that uses stealth tactics as a kernel module to hide. You can read about here:
We do not have a copy of Drovorub to test detection yet, but we will be adding more capabilities to sandfly-processdecloak to decloak other LKM rootkit variants. As LKM rootktis are based on common hiding tactics, the currently released tool will work against a variety of rootkits deploying similar hiding techniques. When we get a copy of Drovorub we’ll be sure to add updates to decloak it as well if not seen already.
sandfly-processdecloak is a utility to quickly scan for Linux Process IDs (PIDs) that are hidden by common and not-so-common loadable kernel module stealth rootkits and decloak them so they are visible.
The tool leverages a Process ID (PID) bruteforce tactic to find processes that are not showing themselves in the standard /proc directory listing on Linux. LKM rootkits often hide entries in /proc because processes not visible in /proc will not be visible with standard system tools like ps, netstat, and so on.
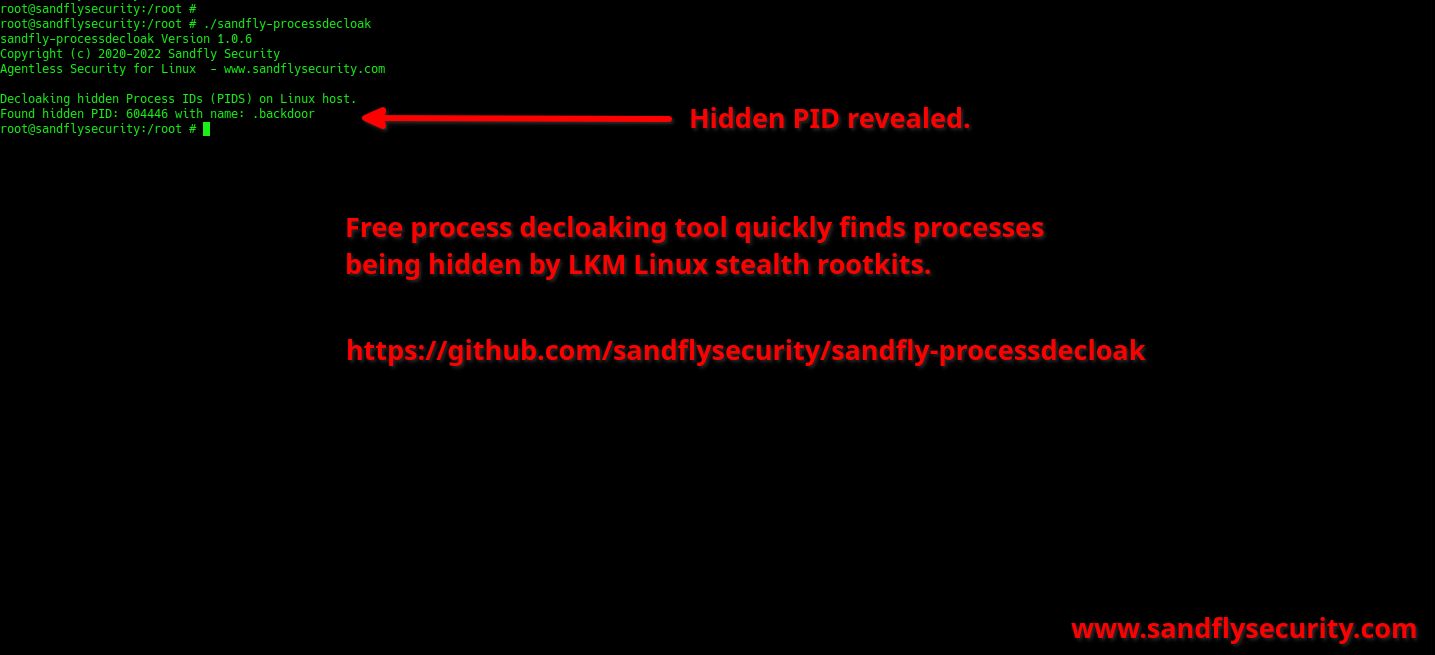
sandfly-processdecloak will analyze the entire valid Linux PID space to check that each running PID in fact is visible as it should be. Processes that are trying to hide are revealed with their PID and process name they are currently using. See examples below.
Simply build and run sandfly-processdecloak for your preferred Linux platform using the built in scripts. Copy the binary onto your hosts you want to check and run it. Hidden PIDs will be shown if found.
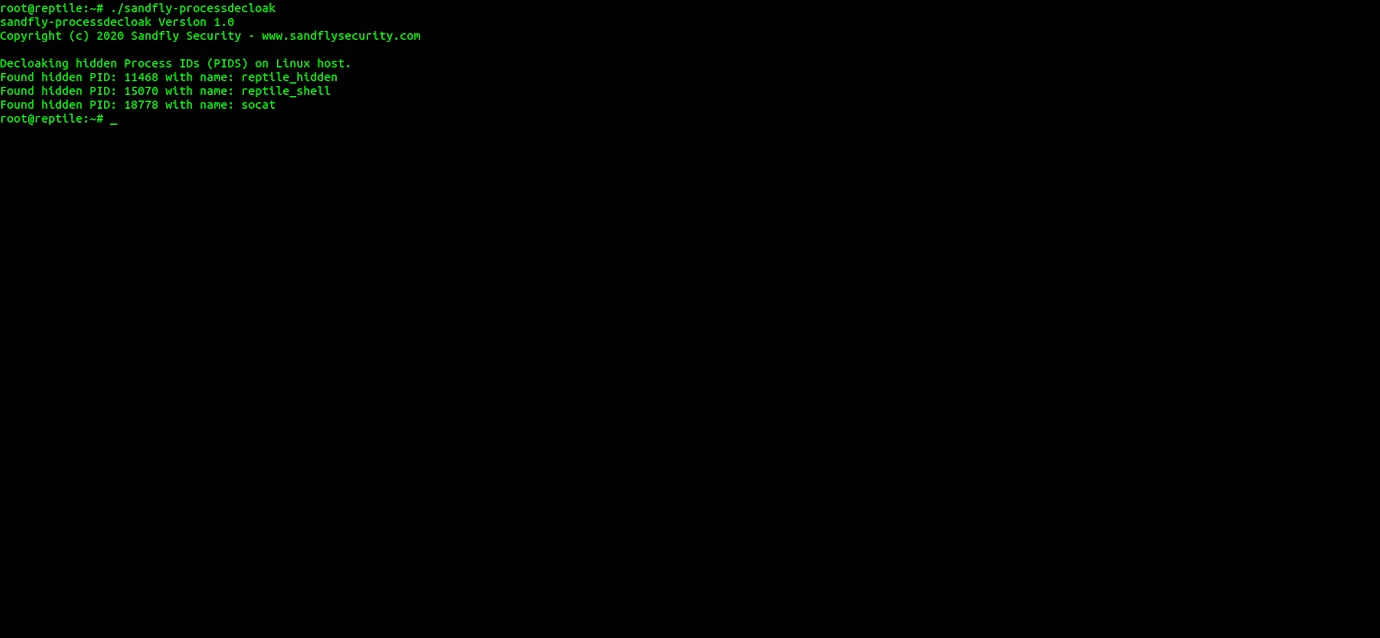
When run, the program will show all clean or PIDs that are suspicious. Below we show the Reptile rootkit hiding the built-in backdoor reptile_shell, a test process called reptile_hidden and a socat program being run as another backdoor.
root@sandfly-clean:~# ./sandfly-processdecloak sandfly-processdecloak Version 1.0
   Copyright (c) 2020 Sandfly Security - www.sandflysecurity.com

   Decloaking hidden Process IDs (PIDS) on Linux host.
No hidden PIDs found.root@sandfly-reptile:~# ./sandfly-processdecloak sandfly-processdecloak Version 1.0
Copyright (c) 2020 Sandfly Security - www.sandflysecurity.com
Decloaking hidden Process IDs (PIDS) on Linux host.
Found hidden PID: 11468 with name: reptile_hidden
Found hidden PID: 15070 with name: reptile_shellroot@sandfly-diamorphine:~# ./sandfly-processdecloak sandfly-processdecloak Version 1.0
Copyright (c) 2020 Sandfly Security - www.sandflysecurity.com
Decloaking hidden Process IDs (PIDS) on Linux host.
Found hidden PID: 7171 with name: diamorphine_hidIt’s possible to flag a legitimate PID that is not actually cloaked but we’ve taken measures to limit this risk. At Sandfly we hate false positives and do everything we can to reduce or eliminate them to not waste your time. Please report false positives to us if you find them.
Sandfly uses a variety of methods to detect and decloak LKM style rootkits in more extensive ways than this free tool does. Not only can Sandfly decloak hidden PIDs, but we also can detect cloaked data in files, cloaked directories and more. Because we are an agentless product, we are able to get onto a large number of Linux hosts to investigate them for LKM rootkits without any system impacts or risks to system stability. Simply point Sandfly at the hosts you want investigated and we’ll do the rest in seconds.
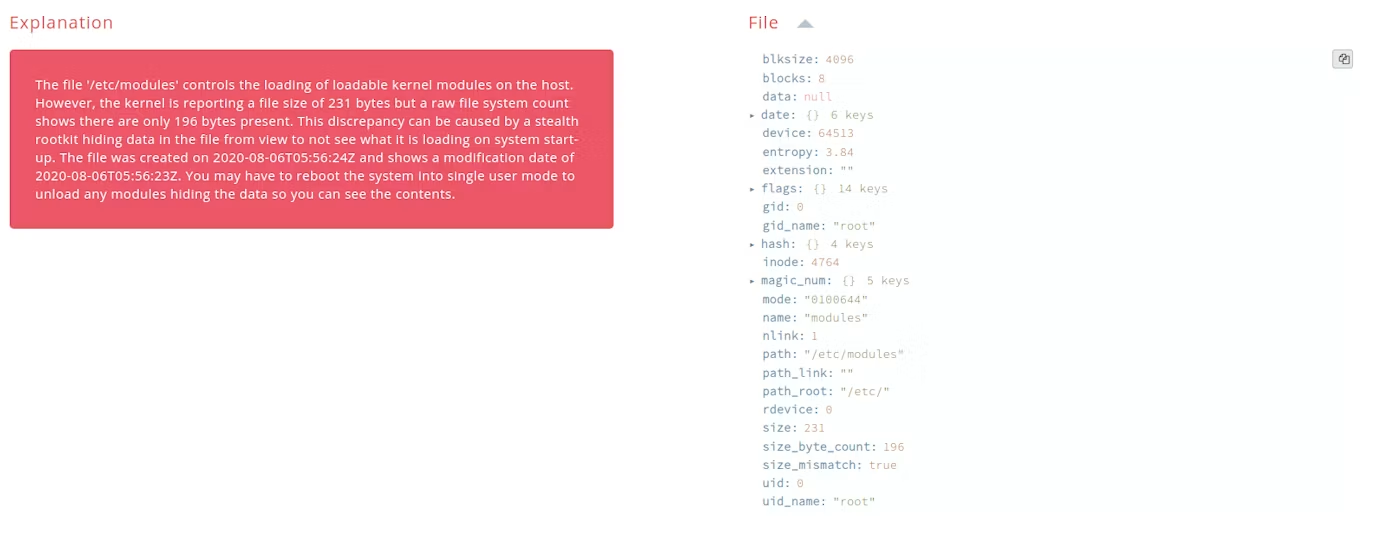
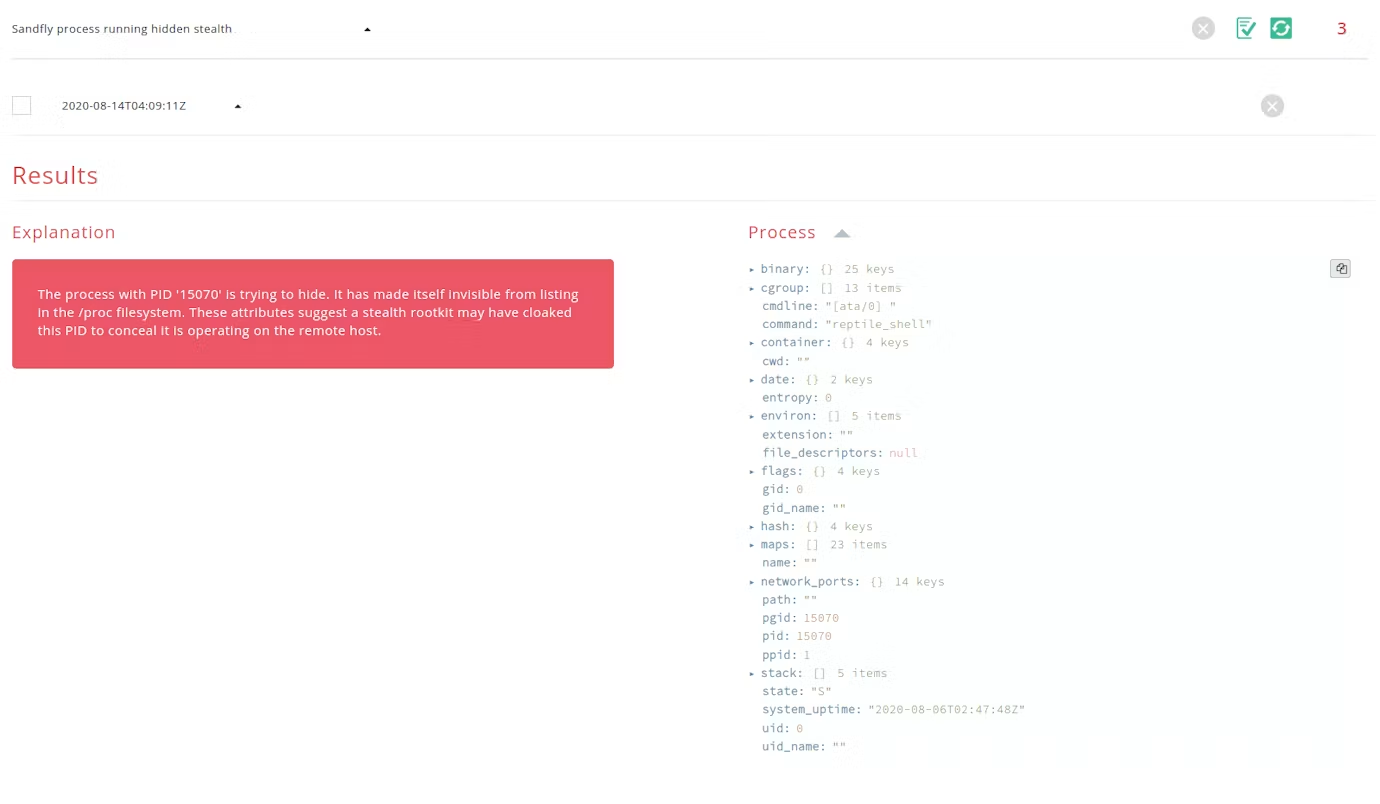 We do further checks in critical system areas for files loading kernel modules but are hiding this data from view.
If you’d like to see a demo of Sandfly and get a free trial, contact us.
1 min read
Publication Date: 30 March 2020