1 min read

Linux Forensics Tools | Intrusion Detection, Threat Hunting & Malware Detect Linux Commands Cheat Sheet

Linux Forensics Tools | Intrusion Detection, Threat Hunting & Malware Detect Linux Commands Cheat Sheet

Publication Date: 26 April 2018


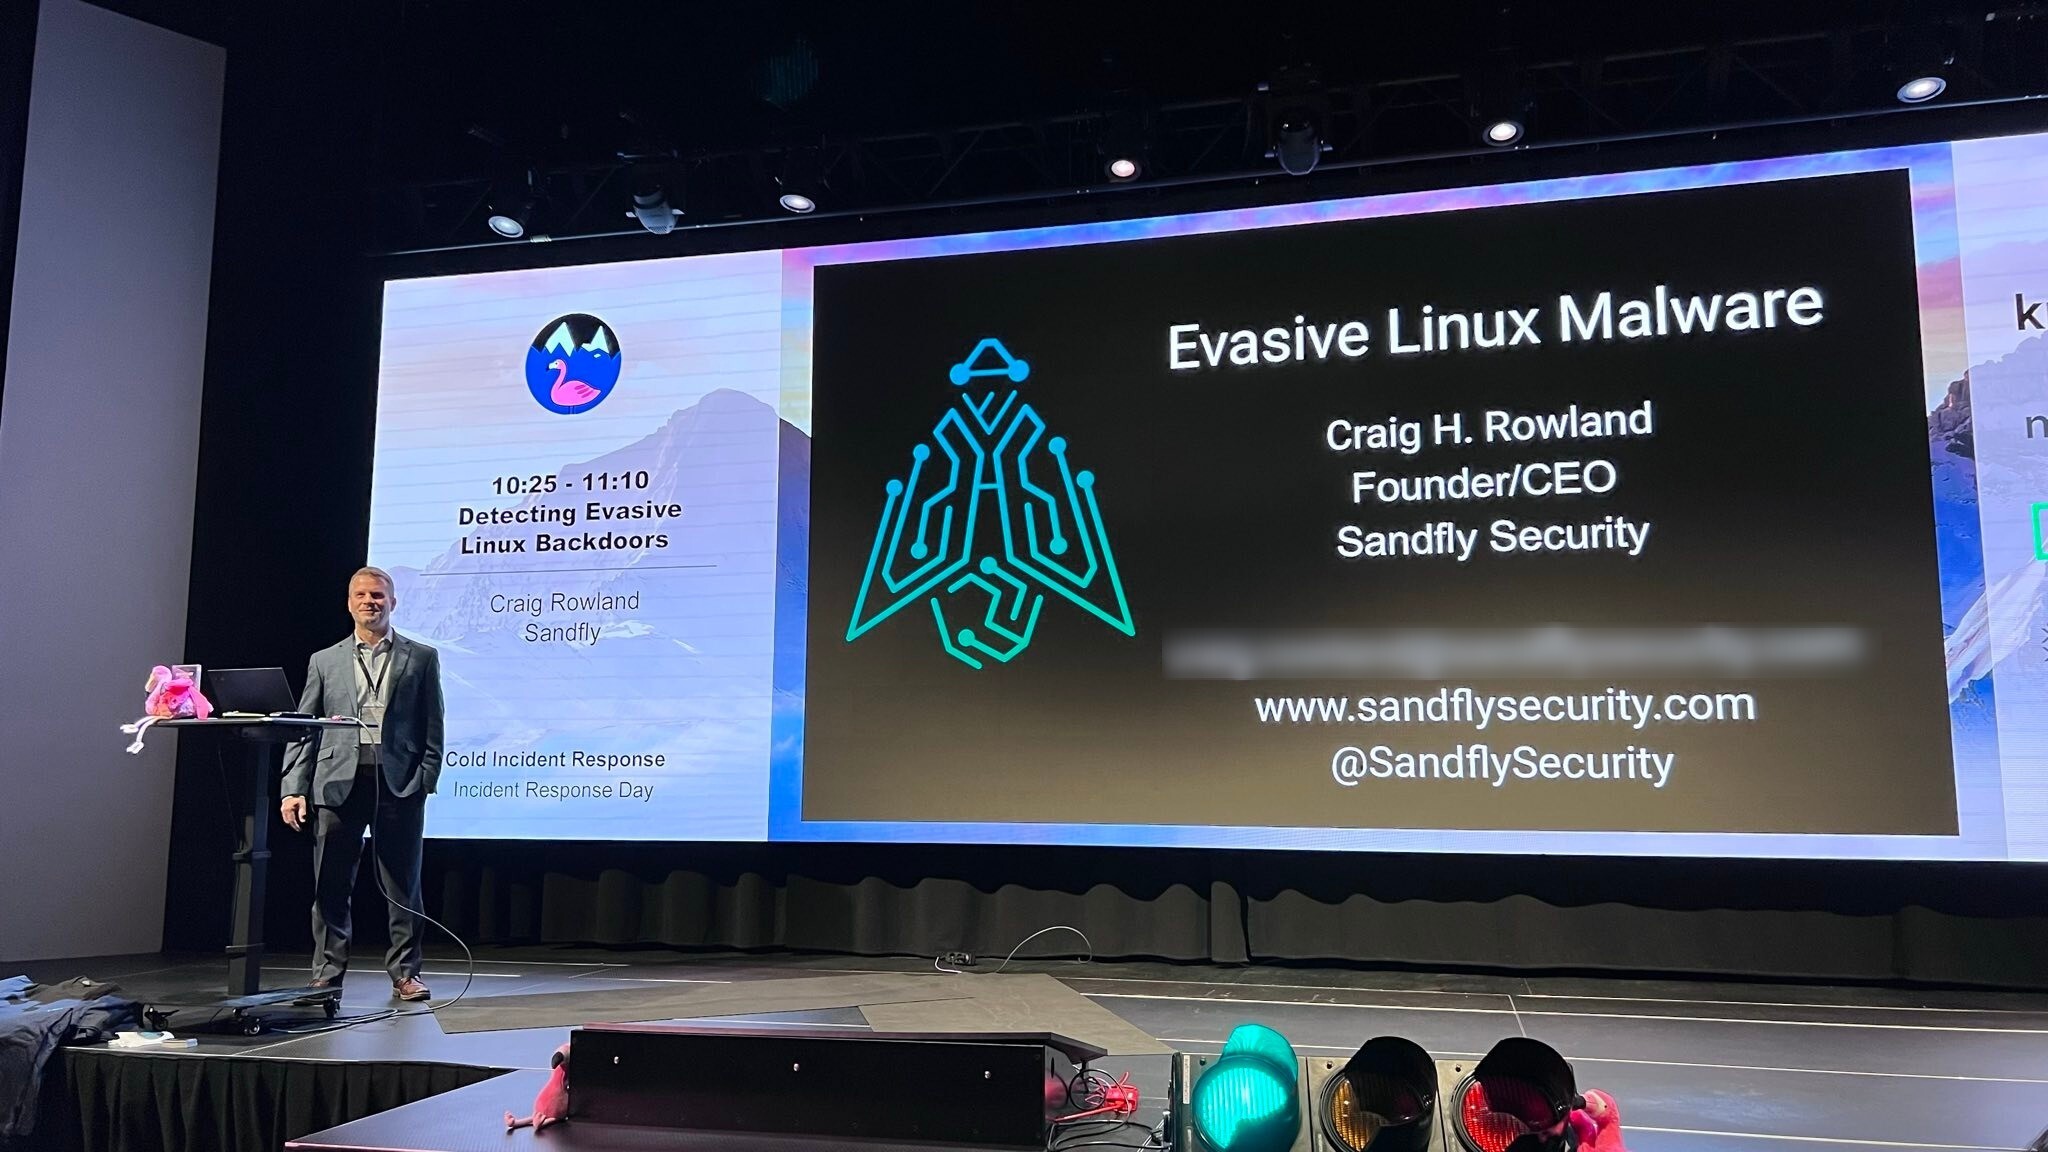
Craig Rowland presented last October at the Christchurch HackCon on the topic of using basic command line tools for Linux forensic investigation and threat hunting. His talk focused around detecting indicators of compromise and malware without the use of expensive intrusion detection and forensics tools.

These slides present basic techniques any Linux administrator can use today to quickly assess a system for common signs of compromise. This includes Linux rootkits, malware, and worms.

Sandfly Security Command Line Linux Forensics

We’d like to thank the hosts of ChCon for the opportunity to speak and great job they did organizing the event.

Sandfly is a specialised linux forensics tool designed to automates the detection of things like malware and ransomware on your Linux systems. It supports all of the most popular distributions including Debian, Ubuntu, Redhat, Suse, Fedora, Arch Linux, CentOS and even Rasberry Pi. Talk to one of our experts and see how Sandly can complete your intrusion detection toolkit.


Linux Forensics Tools | Intrusion Detection, Threat Hunting & Malware Detect Linux Commands Cheat Sheet

Download the free cheat sheet of Linux Forensic commands Tools for threat hunting and help spot compromised hosts, detect intruders, detect malware,...
Read More
Detecting Linux Kernel Process Masquerading with Command Line Forensics

Detecting Linux Kernel Process Masquerading with Command Line Forensics

How to detect Linux kernel process masquerading with simple command line forensics. De-cloak Linux stealth malware quickly and easily.

Read More
Detecting Evasive Linux Malware Presentation

Detecting Evasive Linux Malware Presentation

A presentation on how to detect evasive Linux malware and backdoors using command line forensics.

Read More