Agentless EDR and Linux Threats: Sandfly on the Google Cloud Security Podcast
1 min read
Sandfly Security - Agentless Linux EDR and Incident Response : Published Updated
13 May 2025
Sandfly CEO Craig Rowland was recently featured on the CISO Series podcast "Security You Should Know" in the episode, "Getting Linux Visibility with Sandfly Security."
The episode explores why Linux often flies under the radar in security programs despite powering our most critical systems. Craig explains how legacy servers, embedded systems, and the misconception that Linux is "secure by default" create dangerous visibility gaps.
Craig discusses how Sandfly's agentless approach solves critical Linux security challenges including:
Guest experts Jerich Beason (CISO at WM) and Steve Zalewski (podcast host and CISO) join the conversation to validate why this approach matters for securing modern environments. You’ll gain practical insights into how security professionals can achieve better Linux security without operational drama.
Agentless EDR and Linux Threats: Sandfly on the Google Cloud Security Podcast
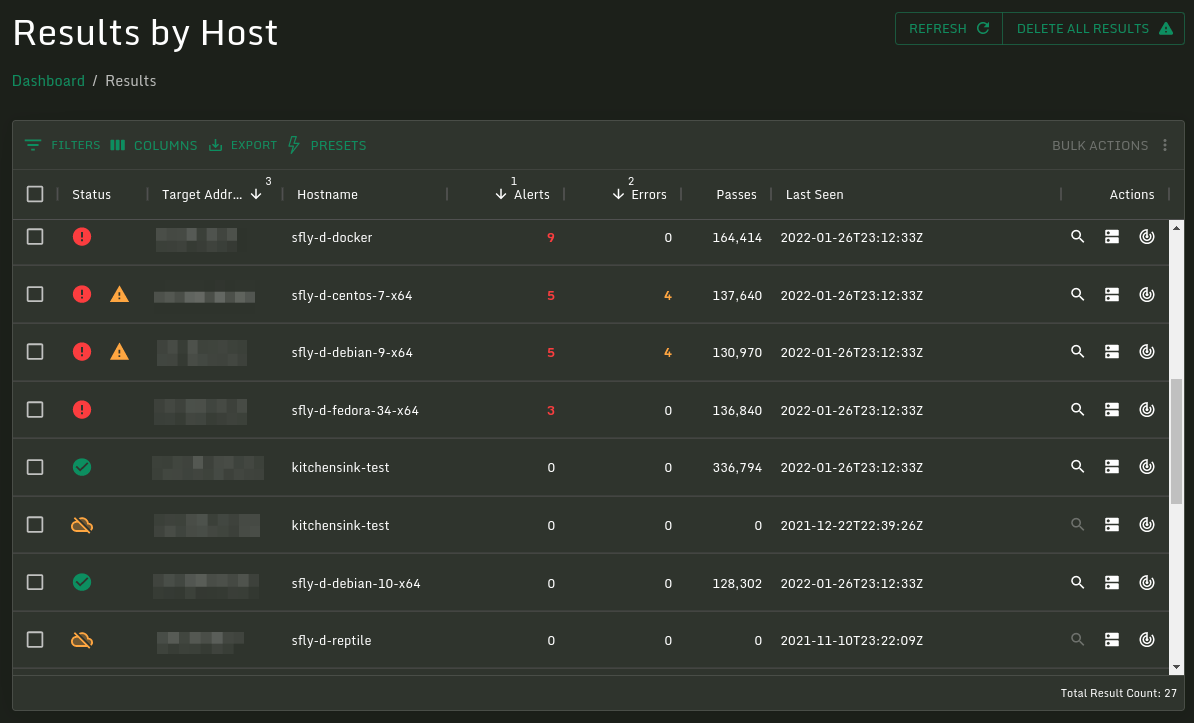
Experienced SOC operator writes about how Sandfly helped them get greater Linux security visibility.
Ericsson uses Sandfly's agentless Linux Endpoint Detection and Response (EDR) to strengthen telecom security globally.